Hintze Law Global AI Legal Updates

Hintze Law’s Global AI Update provides a curated overview of key AI-related legal and regulatory updates. We spotlight new developments and emerging trends to help organizations that are developing, deploying, or relying on AI technologies to stay ahead of what’s next. 

Please also check out our latest Global Privacy Updates post. 

If you’d like to receive email alerts for our blog posts, visit our blog page to sign up. 


US AI Updates  

Amazon v Perplexity and CFAA Injunction Ruling

Amazon had requested a preliminary injunction against Perplexity to prevent Perplexity's AI agent from accessing Amazon.com.

On August 4, 2026, the Ninth Circuit vacated a district court ruling granting the preliminary injunction and ruled that Amazon is "unlikely to succeed on the merits of the "access" prong of the Computer Fraud and Abuse Act (CFAA) and California’s Computer Data Access and Fraud Act (CDAFA) analysis and the equity factors do not otherwise favor an injunction." Rather, the Ninth Circuit held that the user “accesses” Amazon’s computers with the help of the AI agent—Perplexity’s servers never access Amazon’s.

In a footnote to this ruling, the Ninth Circuit confirmed that Amazon may have a separate claim regarding violation of its terms of use (consistent with recent Supreme Court rulings on similar CFAA claims): "This outcome does not impair Amazon’s ability to regulate access to Amazon.com via private terms of service for its users.  On the facts before us, Amazon is simply unlikely to succeed in its attempt to regulate access by invoking the CFAA and the CDAFA."

Federal Court Denies Motion to Dismiss Class Action Against AI Notetaking Tool

On August 13, 2026, N.D. Cal. largely denied Otter.ai’s motion to dismiss, allowing most claims in a class action filed in 2025 to move forward. Plaintiffs had alleged Otter’s “Notetaker” tool recorded, transcribed, retained, and commercially used their private conversations without consent

  • Five major claims survived Otter’s motion to dismiss in full, alleging:

o      ECPA § 2511 + California equivalent (CIPA § 631): Otter intercepted communications in real time and may have used those communications for its own purposes (e.g., machine learning and model training), not just for its users’ benefit, so the party exception would not apply.

o      Illinois BIPA: Otter collected and retained identifiable voiceprints without required notice and consent.

o      California unfair competition: Because individuals can sell or monetize their own data, Otter’s interception of their data and private conversations decreases the market value of such data.

o      California unjust enrichment: Otter received and unjustly retained benefit of significant revenue by, e.g., using plaintiffs’ data for product improvement, at the expense of plaintiffs’ privacy rights

  • Court granted leave to amend all dismissed claims, for example:

o      Federal CFAA claims and California state law counterpart (CDAFA)

§     Plaintiffs didn’t allege “facts explaining how Otter Notetaker supposedly [accessed] any part of their computers, such as ‘files, folders, or databases.’”

§     Alleged injuries of “emotional harm and the alleged loss of value of Plaintiffs’ personal information” are not valid injury for CFAA purposes.

o      Washington equivalent of ECPA

§     Washington plaintiffs failed to allege facts “supporting the reasonableness factors to determine whether a communication is private.”

o      State intrusion on seclusion, invasion of privacy claims

§     Dismissed to extent plaintiffs didn’t allege facts that the nature of the intruded-upon conversations meant that their alleged intrusion was “highly offensive to a reasonable person.”


Courts remain willing to scrutinize AI transcription and meeting-assistant tools, particularly where voice data, model training, retention practices, and consent are at issue. See Jennifer Ruehr’s 10 Ways To Avoid Privacy Risks Revealed In AI Notetaker Suits - Law360.


Meta AI Glasses Class Action Filed

On August 31, 2026, plaintiffs filed an amended complaint for a consolidated class action lawsuit filed against Meta and Luxottica in the northern district of California. The lawsuit alleges that Meta AI Glasses collect, transmit, and use sensitive user and bystander data in ways that were not adequately disclosed to consumers. The complaint challenges Meta's marketing claims that the glasses were "designed for privacy" and "controlled by you," alleging that recordings and captured content were routed to Meta's systems and reviewed by human annotators as part of AI development efforts.

The plaintiffs also allege that the glasses can be activated unintentionally, potentially capturing sensitive information, including private conversations, financial information, medical discussions, and images of individuals who were unaware they were being recorded. The lawsuit further raises concerns regarding bystander privacy, alleging that individuals may have been recorded without knowledge or consent.

The complaint asserts a broad range of federal and state law claims, including consumer protection, privacy, wiretapping, biometric privacy, product liability, and unfair competition causes of action. Plaintiffs seek damages, injunctive relief, and changes to Meta's data collection and AI training practices.


Character.AI Files for Bankruptcy

On October 12, 2026, Character.AI announced that it had voluntarily filed for Chapter 11 bankruptcy, citing significant legal, regulatory, and operational headwinds and leaving its platform available for now. A press release elaborated that bidding procedures "designed to achieve the highest or otherwise best offers for the Company’s assets and [seeking] approval to designate Disney a stalking horse purchaser for certain of the Company’s assets," have been proposed.

NIST Blog Identifies Five Identity and Authorization Risks in Agentic AI Deployments

On August 27, 2026, NIST's National Cybersecurity Center of Excellence (NCCoE) published a Cybersecurity Insights post "Back to the Future" on identity and authorization for AI agents, drawing on public comments to its concept paper on software and AI agent identity and authorization.

The argument is that agentic deployments are not generating wholly novel security problems so much as reintroducing familiar identity and access management (IAM) failures at machine speed. The post names five patterns:

1.      Sharing human credentials with agents, which creates accountability gaps that matter most where non-repudiation is a control (financial transactions, health data);

2.      Static, long-lived API keys and bearer tokens, which carry no proof of possession and often sit in the clear in config files and logs;

3.      Broadly scoped entitlements, which agents will probe and act on more quickly and less predictably than humans;

4.      Deploying agents under local user accounts, which lets them impersonate the user and defeats central identity management; and

5.      Over-reliance on human-in-the-loop (HITL) approval, which breeds the same reflexive clicking as multi-factor authentication push bombing.

NIST's position is that existing standards—including OAuth 2.0, SPIFFE, and sender-constrained tokens—are adequate foundations today, and it points to NISTIR 8587 on token management (finalized on September 15, 2026, further posts and publications in the series are planned).

None of this is binding, but it is a workable baseline for an organization’s AI governance: give agents their own identities bound to a responsible human, scope and time-limit their credentials, and treat elicitation prompts as a channel that should never carry credentials or sensitive data.

NAI Published Voluntary Guidance on AI Use in Network Advertising

On July 20, 2026, the Network Advertising Initiative (NAI) published Key Do's & Don'ts for Using AI in Network Advertising, a voluntary guidance document for its ad-tech members. There is no compliance deadline or enforcement date.

The guidance does not add controls for the machine learning, optimization, and predictive modeling already governed by the NAI Framework. It targets two newer categories: generative and broadly adaptive systems, including natural-language audience creation tools, and agentic workflows in which systems access data, bid on inventory, and execute transactions without a human approving each step. Recommendations scale with a system's autonomy.

Nine topics are covered:

1.      Inventory and enabling of AI use cases

2.      Advertising audience/segment review and activation

3.      Testing and monitoring of AI systems

4.      Disclosures about how AI systems are used

5.      Permissions and constraints applied to AI systems

6.      Choice and signal handling

7.      Oversight and logging for agentic AI systems

8.      Contracting and risk allocation between AI users and AI vendors

9.      Accountability

Ad-tech clients should inventory AI-enabled tools and categorize them by level of autonomy; screen AI-generated segments against a sensitive-vertical list before activation, including for inadvertent proxies; confirm that opt-out and preference signals such as Global Privacy Control (GPC) are preserved across intermediaries and orchestration layers; and revisit vendor contracts to allocate AI-specific responsibility, including whether workflow-exposed campaign and audience data may be reused for fine-tuning or general training. The guidance document closes with a one-page checklist of nine working questions.

CA Governor Issues AI Oversight and Safety Executive Order

On September 18, 2026, the CA Governor announced the issuance of Executive Order N-9-26 “to dramatically accelerate the implementation of new third-party oversight of safety and security risks in AI systems, as well as independent audits.”

In addition to summarizing enacted CA legislation and efforts relating to AI, the press release notes that the executive order convenes a group of experts to provide California a guide for its AI safety and security laws within two months and directs the Government Operations Agency to accelerate the implementation timelines for SB 813 and AB 1405.

SB 813 establishes “a framework for independent verification organizations that can assess AI systems and models for safety and risk.” Its requirements for the Government Operations Agency and AI auditors (“Independent verification organization” or “IVOs”) which the agency has designated as having demonstrated expertise in AI risk assessments include:

  • Requiring the agency, on or before January 1, 2028, to develop criteria for determining whether an AI auditor qualifies as a designated IVO and criteria for whether to grant or remove such designation.

  • Requiring a designated IVO to submit annual reports to the agency and legislature of its standards and methodologies and of any changes to its governance policies or sources of funding.

Beginning on January 1, 2029, AB 1405 creates “a state registry for AI auditors that assess AI systems and models for compliance with state law and establishing standards for their independence, transparency, and integrity.” A person may not offer, sell, or conduct a covered AI audit unless they have registered. The audits must also meet requirements as stated by the law.

California Passes Twin AI Transparency Laws

On September 30, 2026, California passed SB 1000 and AB 2713, amending the California AI Transparency Act. Key changes include:

SB 1000

  • Expanded covered-provider scope. SB 1000 removes the Act’s existing threshold of more than one million monthly visitors or users from the definition of “covered provider.”

  • Revised verification tool requirements. SB 1000 replaces the existing “AI detection tool” terminology with a “disclosure verification tool” and modifies its requirements by expressly permitting providers to rely on compliant third-party verification tools to meet the verification tool requirement. It also excludes alterations consisting only of specified “minor modifications” from the tool’s assessment of whether content was created or altered by the provider’s system. "Minor modifications" are defined as the following alterations: changes to brightness, contrast, or color; sharpening or saturation; resizing or scaling; cropping; file-format conversions; and certain audio denoising. 

  • Expanded latent provenance disclosure requirements. SB 1000 expands the latent disclosure requirement by requiring: 

o      Providers to include latent disclosures in content that is created or altered by genAI systems, previously only applying to content "created by" genAI systems under SB 942. It also includes an exception for “minor modifications,” which do not need latent disclosures.

o      Providers to include in the provenance data whether the system created or altered the content.

o      Latent disclosures, where not permanent, to be extraordinarily difficult to remove or tamper with, adding tamper resistance to the existing requirement.

o      Latent disclosures to be "compliant or interoperable" with widely recognized industry standards, replacing SB 942's requirement to be "consistent" with such standards.

  • Eliminated manifest disclosure requirement. SB 1000 eliminates the requirement that providers offer users the option to include a manifest disclosure identifying content as AI-generated.

  • Revised third-party licensing requirements. SB 1000 significantly revises the existing third-party licensing framework. It introduces an obligation for providers to notify licensees of their obligations under the Act. If a provider knows that a licensee modified the genAI system so that it no longer complies with the Act, the provider must, within 72 hours, either terminate the licensee's authorization or notify the licensee of the noncompliance and that continued noncompliance must be reported to the AG. If notified, the licensee must bring the system into compliance or cease using or making it available, and report the action taken to the provider within 96 hours. If the licensee fails to provide that report, or reports that it did not remediate or cease use, the provider must report the noncompliance to the AG. The Act does not require providers to monitor, investigate, or otherwise inquire into a licensee’s use or modification of a licensed system.

  • Other changes. SB 1000 also makes additional changes concerning the output of personal information by disclosure verification tools and requirements for genAI systems designed primarily to function as assistive technology.

AB 2713

  • Clarified applicable provenance standards. AB 2713 specifies that large online platforms are not required to take any action with respect to provenance data that is not compliant or interoperable with widely adopted specifications issued by an established standards-setting body.

  • Expanded platform provenance detection requirements. AB 853 requires large online platforms to detect provenance data that is embedded into or attached to content. AB 2713 expands this requirement to provenance data that is also "otherwise associated with" content. The law does not define what constitutes provenance data that is “otherwise associated with” content, leaving some uncertainty regarding the practical scope of this expanded requirement. The language may be intended to accommodate current or future additional technical methods of associating and tracking provenance information.

  • Expanded provenance preservation requirements. AB 2713 expands the existing prohibition on knowingly stripping provenance data from content uploaded to or distributed on a platform to also cover content downloaded from the platform, to the extent technically feasible. 

California Workplace Surveillance Law AB 1883 Passed

On September 30, 2026, California enacted AB 1883, updating Division 2 of the Labor Code to prohibit employers' use of "workplace surveillance" tools that use AI for (1) "Recognizing, or making inferences or predictions about, an individual’s emotional state; or (2) Collecting neural data."

The law will be enforceable by either California's Labor Commissioner or a public prosecutor. Violations are subject to civil penalties of up to $500 for each violation.

CT AG Reminds Consumers of Privacy Rights Entering into Effect

On September 16, 2026, the Connecticut AG published a reminder that, under amendments entering into effect on October 1, 2026, of additional privacy rights, "related to artificial intelligence, Facial Recognition Technology (FRT), genetic data privacy, surveillance pricing, and data brokers, as well as through recent amendments to the Connecticut Data Privacy Act (“CTDPA”)."

Under SB4, the AG highlighted the following rights and requirements:

  • Limitations on surveillance pricing as well as disclosure requirements for businesses using personal data in price settings;

  • Limitations on and disclosure requirements for the use of FRT, including requiring that companies post clearly legible signage alerting consumers that FRT is in use on the premises and providing them with a conspicuous hyperlink or quick response code directing them to the company’s facial recognition technology policy;

  • Limitations and consent obligations for Direct-to-Consumer Testing Companies that are collecting consumer’s genetic data, including providing consumers with a property right and exclusive control over the collection, use, retention, maintenance, disclosure, and destruction of the sample and result;

  • Further limitations on what is considered publicly available information as well as expanded consumer data deletion rights related to consumer profiles generated from publicly available information;

  • A ban on the sale of consumer’s precise geolocation data; and

  • The creation of a data broker registry which requires data brokers to register with the Connecticut Department of Consumer Protection by January 1, 2027.

Under SB5, the AG highlighted the Connecticut Artificial Intelligence Responsibility and Transparency Act (“CART Act”) with the following rights and requirements:

  • Chatbots and Kids

o      Companies that offer chatbots to children must put a protocol in place to detect and address chats indicating a risk of self-harm;

o      Chatbot platforms must offer parental controls;

o      Chatbots are prohibited from sending harmful communications to children;

o      Chatbots cannot encourage children towards physical violence, substance abuse, or disordered eating; and

o      Companies that offer chatbots to children cannot allow their chatbots to engage in romantic or sexual interactions with children or use manipulative engagement mechanics to keep them using the platform.

  • AI and Employment

o      Employers must provide written notice when using AI to make a decision that impacts terms, privileges, or conditions of employment; and

o      Employers are prohibited from using AI to discriminate against employees, and any such discrimination is considered employment discrimination that is also violative of the Connecticut Fair Employment Practices Act.

New Mexico Unveil Frontier AI Legislation Ahead of 2027 Legislative Session

On October 1, 2026, Attorney General Raúl Torrez and State Representative Linda Serrato announced the Frontier Artificial Intelligence Safety Act (summary here), in response to cybersecurity incidents where AI agents accessed systems without authorization or explicit instruction.

The proposal looks to complement other frontier AI model legislation, California's Transparency in Frontier Artificial Intelligence Act (SB 53, effective January 2026), New York's RAISE Act (effective January 2027), and the EU AI Act, and share many obligations while tightening others:

  • Framework, risk-assessment, and transparency-report obligations

  • Reporting within 72 hours of any critical safety incident, and 24 hours for a loss-of-control or autonomous cyber-offense incident.

  • Third-party audits of a developer's own risk assessment, narrowed to the specific risk categories tied to the incident.

  • Export-control-style know-your-customer and anomalous-use duty for large compute providers.

  • Pre-training notification.

  • Damage and liability based remedies, in contrast to NY and CA.

If the proposal passes, it will be effective July 1, 2027.

Colorado AG Publishes Interim Draft Rules for Chatbots & Automated Decision-Making Technologies (ADMT)

On October 6, 2026, the DOL released an interim draft of the ADMT and Chatbot Safety Rules, which clarify and implement Senate Bill 26-189 and House Bill 26-1263, and a cover page with additional considerations. 

Notably, the ADMT rules state that a party that integrates existing Covered ADMT into its own Covered ADMT product and provides its own Covered ADMT product to another Developer or a Deployer and a Developer that integrates existing Covered ADMT into its own Covered ADMT and provides its own Covered ADMT product are considered "Developers." Along with examples for education, employment, real estate, and financial services, the rules have provisions for ADMT use including:

  • Requiring ADMT developers to create and maintain documentation and disclose to a Deployer (Deploy defined as use of Covered ADMT in, run directly or through a third-party, to make a Consequential Decision) the Covered ADMT’s known limitations, known risks, and circumstances under which the Covered ADMT should and should not be used.

  • Providing that the presumption that ADMT output Materially Influences a Consequential Decision may be rebutted with evidence that the output was a de-minimis factor in the decision.

  • Requiring Deployers to provide ADMT Adverse Outcome Disclosures, which must contain a plain language description of the Consequential Decision and the role the Covered ADMT played, instructions to request additional information about the Covered ADMT, an explanation of the Consumer Rights and how to exercise them.

  • Requiring Deployers to process Consumer Rights (Right to Access/Correct Personal Data used in the Consequential Decision and Meaningful Human Review) after the Deployer uses a commercially reasonable method for authenticating the consumer's identity.

The Rules also have provisions for Operators of Conversational Artificial Intelligence Services, including:

  • Requiring the use of commercially reasonable methods or generally accepted methods to estimate the age of Account Holders or Users of Conversational Artificial Intelligence Services, such as an ISO/IEC 27566-1:2025 and, where applicable, 5IEEE 2089.1 compliant age assurance system or method; a cryptographic technique, such as a zero-knowledge proof; matching a scan of a government-issued ID and live photo or video using facial recognition; or signing in with an authenticated, school-provisioned account.

  • Requiring the disclosure to the user that they are interacting with artificial intelligence.

  • Requiring the provision of tools to minors and their parents to control privacy and safety settings.

  • Requiring the submission of an Annual Report to the Attorney General’s office on or before July 1. The report must include the operator's size, the number of crisis service provider referral notifications reported, the protocols for responding to user suicidal ideation or self-harm risk, age-estimation measures and the sexual-content safeguards.

State AG Coalition Urges Congress to Regulate Large-Scale AI Models/Devs

On September 23, 2026, a bipartisan coalition of 25 state AGs, led by NY and NJ, sent an open letter to Congress urging them to regulate large-scale AI models and developers. The letter discusses the recently-reported AI safety incidents (e.g., Open AI / Hugging Face), the shortcomings of self-regulation, recent support for regulation by developers, and a list of recommended features that a national framework for regulating large-scale AI models would address (e.g., safety testing and standards, government-led incident response, no preemption of state laws). 

The letter is signed by a mix of states with and without AI-specific or comprehensive privacy laws, such as AZ, CA, CO, CT, DE, IL, MD, MN, NV, VA, and WA. In announcing his signature on the letter, the California AG emphasized California's ongoing legislative/enforcement work to ensure AI safety.


Global Updates

European Telecommunications Standards Institute Publishes AI Data Quality Standard

On September 3, 2026, the European Telecommunications Standards Institute (ETSI) announced a framework to assess "the quality of data used across digital and AI ecosystems." The framework's 18 metrics can be put into four categories:

Fundamental data quality: including completeness, accuracy, reliability, consistency, precision, integrity, redundancy and uniqueness.

Usability: including availability, coverage, lineage, traceability and timeliness.

Fairness: including label quality, measurement bias and representation bias.

Privacy and responsible data use: including anonymity and confidentiality.


European Commission Designates ChatGPT as a Very Large Online Search Engine Under the DSA

On August 31, 2026, the European Commission designated ChatGPT as a Very Large Online Search Engine (VLOSE), and designated Reddit and Roblox as Very Large Online Platforms (VLOPs). Each service declared that it reaches at least 45 million average monthly users in the EU, meeting the designation threshold.

According to IAPP: “The designation brings additional DSA requirements for systemic risk assessment and mitigation, children's online safety and preservation of fundamental rights, which take effect in January 2027.”

Interestingly, the Commission treated ChatGPT as a hybrid service that qualifies as an online search engine under the DSA because it responds to user prompts in part by searching the web. This appears to be the first time a conversational AI assistant has been designated as a VLOSE, with the designation based on its retrieval functionality rather than the underlying model. Reddit and Roblox were designated as platforms on the ground that users disseminate third-party content to the public.

The Commission will supervise compliance alongside Coimisiún na Meán in Ireland for ChatGPT and alongside The Authority for Consumers and Markets in the Netherlands for Reddit and Roblox. The Commission also gains investigative powers over the functionalities behind the services.

Ireland, Poland, and Greece Adopt AI Act Implementation Legislation

Over July 2026, Ireland, Poland, and Greece adopted laws implementing the EU AI Act. The laws establish these countries’ domestic regulatory structures for overseeing AI systems and supporting compliance with the EU AI Act. Organizations developing, deploying, or using AI systems in these countries should monitor implementation guidance and enforcement developments as authorities begin operationalizing the new framework and aligning national oversight with broader EU AI requirements.

China's Supreme People's Court Issues Nationwide Guidance on Artificial Intelligence Disputes

On September 7, 2026, China's Supreme People's Court (SPC) issued 24-article Opinions directing lower courts on how the Civil Code, Personal Information Protection Law, and other existing statutes apply to AI disputes.

China has no dedicated AI statute, so the Opinions show judges how current law maps onto specific AI fact patterns: face swapping and voice cloning, hallucinated content, AI-assisted doxxing, algorithmic price discrimination, driver-assist vehicles, and model training. The SPC calls the document the first set of AI adjudication rules issued by China's top court, deliberately leaving questions where no consensus has formed unaddressed.

Key Takeaways from the SPC Opinions:

  • Fault Liability. Where no strict-liability rule applies, courts will use ordinary fault principles and allocate responsibility among developers, providers, and users based on factors such as system autonomy, foreseeable risks, safeguards, and user control.

  • Privacy and Training Data. Publicly available personal information may generally be used for model training if the use is reasonable and the individual has not objected. Courts will assess necessity, proportionality, data sensitivity, and context. AI-enabled doxxing, surveillance, and other privacy intrusions remain unlawful.

  • Deepfakes and Synthetic Content. Unauthorized use of a person's likeness, name, or voice can infringe personality rights. Providers may face liability if they fail to act after receiving valid notice of infringing content, while users who intentionally generate infringing outputs remain responsible.

  • Consumer Protection and AI Products. Unreasonable algorithmic price discrimination may create liability. Product-liability rules apply to physical AI products such as robots and autonomous vehicles, with courts examining factors including self-learning capabilities, updates, user control, and risk disclosures.

  • Intellectual Property and Data. Courts will allocate copyright liability among developers, providers, and users. Developers may need to prove training-data provenance and model operations. Open-source contributors may receive limited protection if they disclose functions and risks. The SPC left unresolved whether AI-generated content is copyrightable and how unlicensed training on copyrighted works should be treated.

  • AI in Litigation. Courts may draw adverse inferences when parties withhold key electronic evidence. AI-generated evidence will be scrutinized, and fabricated AI evidence can result in sanctions. Parties using AI in court filings must verify accuracy and disclose AI assistance.

  • Implications for Companies. The Opinions make governance, recordkeeping, and training-data documentation increasingly important. Companies should maintain evidence of data sources and development processes, establish notice-and-takedown procedures, review pricing and consent practices, and ensure clear disclosures regarding AI capabilities and risks.

The Opinions apply as of their issuance on September 7, 2026, and do not state a separate effective date.


Slovenia Publishes Guidance on Art 50(2) Transparency Obligations Under EU AI Act

On September 21, 2026, the Agency for Communication Networks and Services of the Republic of Slovenia (AKOS) published guidance on the transparency obligations under Article 50(2) of the EU AI Act for providers of artificial intelligence (AI) systems that create or manipulate synthetic audio, image, video, or text content.

Per the guidance, the provider must highlight the output of the AI system (image, video, sound or text) so that it is labelled in a machine-readable format and detectable as artificially generated or manipulated, even if the output contains human generated or manipulated content. Possible marking techniques include:

  • Watermarks;

  • Metadata tagging;

  • Cryptographic methods for proving the origin and authenticity of the content;

  • Recording methods;

  • Digital fingerprints; or

  • Other appropriate techniques or combinations of those techniques.

These requirements entered into effect on August 2, 2026, and providers of relevant systems placed on the market before that date must comply by December 2, 2026.

Kazakhstan's National Standard for AI Applications Published

On October 8, 2026, Kazakhstan's Ministry of Artificial Intelligence and Digital Development announced the introduction of a national standard for the development and use of AI. The standard, ST RK ISO/IEC 5339-2025, has been in effect since January 1, 2026, and is identical to the ISO Standard ISO/IEC 3559:2024.

Malaysia's Personal Data Protection Department Launches Public Consultation on AI

On October 5, 2026, Malaysia's Personal Data Protection Department (PDP) published Public Consultation Paper No. 1/2026, an Artificial Intelligence and Personal Data Protection Framework, for comment until October 23, 2026. The framework is proposed as a primary reference document to clarify regulatory obligations when personal data is processed through AI, outline best practices regarding personal data processing across AI models, and strengthen data governance throughout AI system lifecycle. 


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.
Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Law Global Privacy Updates

The Hintze Law team continues to monitor global privacy and data security developments to provide timely, practical insights for clients. Below is a summary of key updates from August and September 2026.

For developments in AI, please see our latest Global AI Updates.

If you’d like to receive email alerts for our blog posts, visit our blog page to sign up.


US Privacy Updates  


CalPrivacy Brings First Action Against Data Broker Under CCPA and Delete Act

CalPrivacy announced its first action against a data broker under both the CCPA and Delete act.

The California Privacy Protection Agency (CPPA) has issued its first enforcement decision under both the California Consumer Privacy Act (CCPA) and the Delete Act. The decision requires LocateSmarter LLC, an Iowa-based data broker, to pay $116,490 for failing to register as a data broker and for requiring California residents to provide a partial Social Security number before exercising their opt-out rights.

This marks the first enforcement action taken against a data broker under the CCPA. According to the decision, LocateSmarter collected personal information outside of a direct relationship and sold it to third parties thereby meeting the definition of a data broker. However, it failed to register with the CCPA by the January 31, 2026, deadline. The company also required consumers to disclose the last four digits of their Social Security numbers and their full name and mailing address in order to submit opt-out requests.


CalPrivacy Fines VA-Based Data Broker in DELETE Act Enforcement Action

On September 1, 2026, CalPrivacy announced a fine of $36.4K for SalesIntel Research, Inc. a Virginia-based data broker, based on failure to timely register under the DELETE Act. Like the recent Cybba decision, the order is limited to SalesIntel's failure to register by January 31, 2025, for data broker activities in 2024 (SalesIntel timely registered for its 2025 activities). Also, like Cybba and other recent data broker enforcement actions, CalPrivacy quotes heavily from the defendant's own website and client testimonies to establish it as a data broker (e.g., citing product copy that SalesIntel can provide "[e]very contact['s]... verified email, mobile direct dial, title, seniority, and full org chart context", including California residents). 

In addition to the statutory fine for late registration, the order also requires Cybba to comply with other provisions of the DELETE Act, such as disclosing the required metrics related to CCPA requests in its privacy policy. 


CalPrivacy Shares DROP Results So Far

On August 25, 2026, CalPrivacy announced that over 500,000 California residents have successfully registered for DROP. While the press release is focused on encouraging even more consumers to register, it also includes some interesting stats on DROP results to date: 

  • "654 data brokers are now part of the system, and since the August 1, 2026 deadline for brokers to begin processing requests, approximately 25% have already reported that they processed deletion requests.

  • 99.9% of consumers have already had their profile deleted by at least one broker, and the typical California DROP user has already had their information removed by over 40 brokers."


CCPA Amendment SB 923 Passed into Law

On September 27, 2026, California's passed into law SB 923. SB 923 amends CCPA's right to delete and is sponsored by CalPrivacy. For an official redline of how the bill amends CCPA, see here. Specifically, SB 923 makes the following changes, effective January 1, 2027:

  • Creates a third-party data deletion safe harbor aligned with several other states, which clarifies what complying with a deletion request looks like for data collected from a source other than the consumer. 

  • Clarifies legislative intent about the scope of a consumer's right to delete.


CCPA Amendment Regarding Sensitive Data Vetoed by Governor

  • On September 27, 2026, California's governor vetoed AB 1542. If passed, AB 1542 would have amended CCPA to prohibit businesses, service providers, and contractors from "selling"/"sharing" SPI to third parties. The governor’s letter cites concerns of unintended consequences from removing consumers from the decision process and implementation and enforcement costs not included in the 2026 Budget Act.


California Passes Pixel-Related CIPA Reform

On September 30, 2026, California passed into law SB 690.  SB 690 would somewhat restrict the private right of action in California’s wiretap law (“CIPA”), effective January 1, 2027. This amendment would partially limit CIPA’s private right of action, so that alleged violations of CIPA’s pen register/tap-and-trace restrictions arising from conduct “occurring on an internet website, online application, or mobile application” could only be prosecuted by the California AG. This would also negate “any [such private,] pending claim in an action commenced [on or after January 1, 2025].”


California Passes Online Addictive Features Bill

  • On September 10, 2026, California passed AB 1709, repealing and replacing the Age Appropriate Design Code. The law prohibits “a covered platform, as defined, from providing an addictive feature, as defined, to a user who is under 16 years of age and [requires] a covered platform to implement reasonable measures to ensure that users under 16 years of age are not offered or provided any addictive feature on the covered platform.“Addictive feature” = addictive feed, autoplay, and any features  defined by regulation.

  • “Covered platform” = “an internet website, online service, online application, or mobile application… that offers users or provides users with an addictive feature as a significant part of the service provided by that internet website, online service, online application, or mobile application.” This does not include businesses limited to e-commerce or cloud storage functions

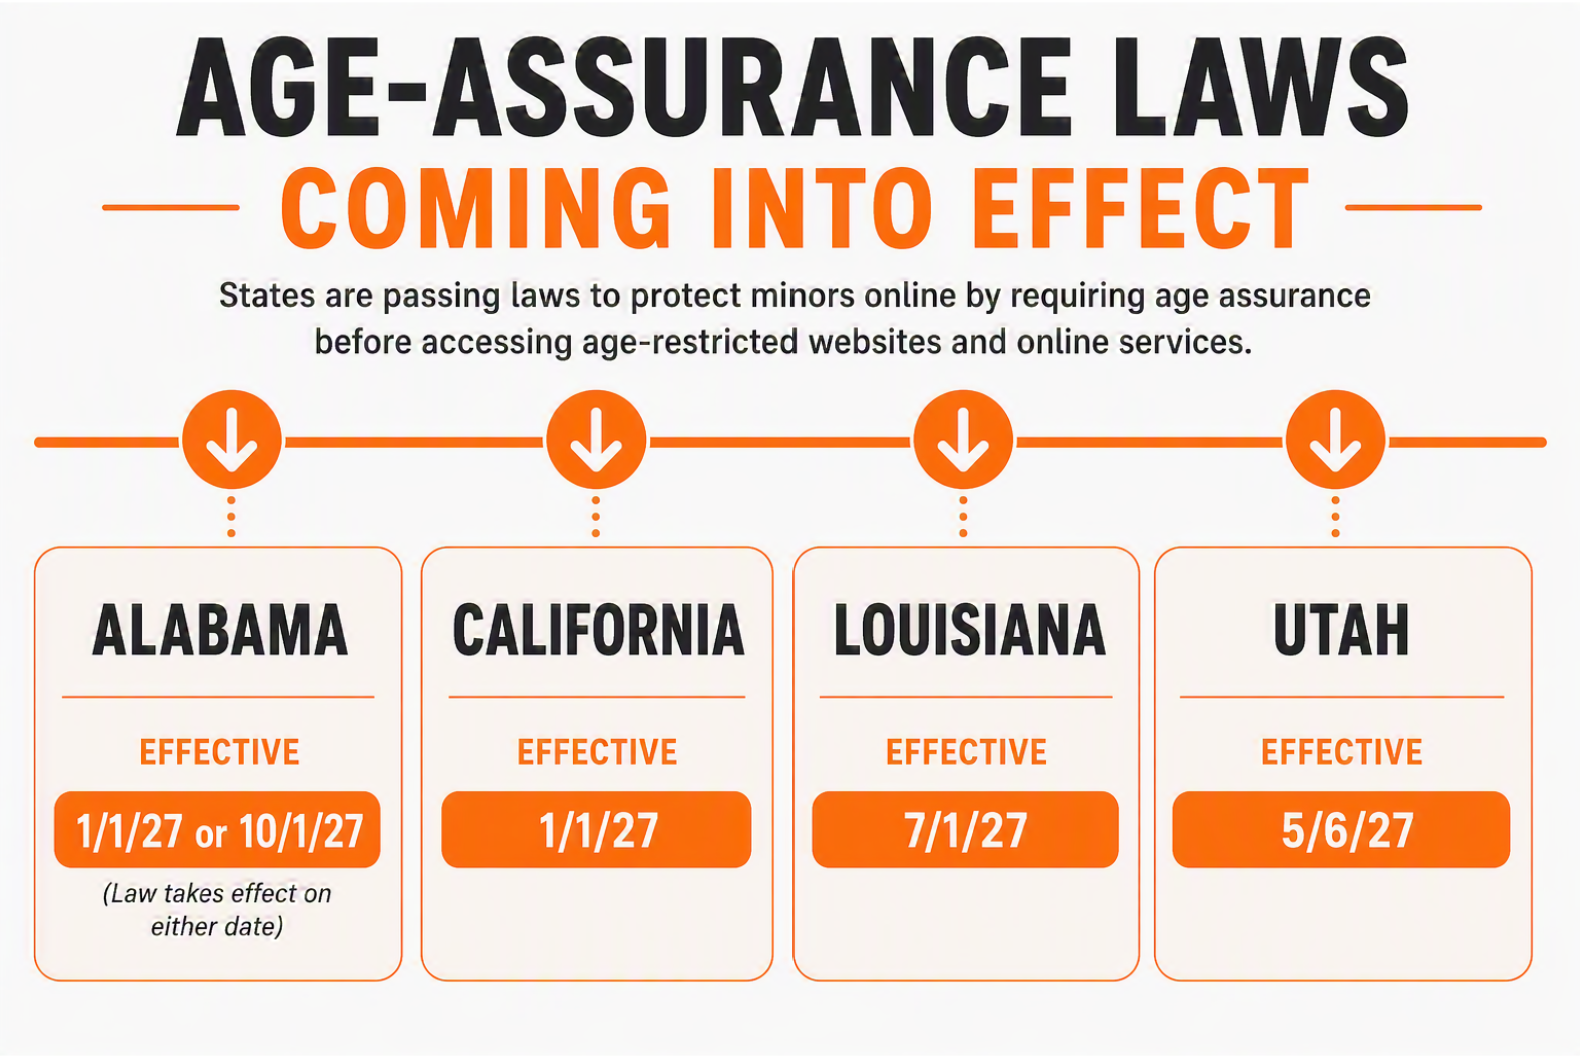
It relies on the California Digital Age Assurance Act for age verification and creates a state advisory commission in the DOJ dedicated to online safety. The law takes effect January 1, 2027, and authorizes the Attorney General to adopt further regulations.


California Legislature Passes Workplace Bathroom Surveillance Law

On September 30, 2026, California passed AB 1331 which restricts employers from monitoring employees in workplace bathrooms and establishes certain employee rights regarding workplace surveillance tools when they enter a bathroom. Similar to the other workplace privacy bills, AB 1883 and SB 947, AB 1331 authorizes enforcement by the Labor Commissioner and public prosecutors and provides for penalties of up to $500 per violation.


California Passes Automated Decision Systems in Employment Contexts Bill

On September 30, 2026, California passed SB 947, which will regulate certain aspects of automated decision systems (“ADS”) in employment contexts.
  
Key requirements include: 

  • Prohibitions on certain uses of ADS, including preventing compliance with federal, state, or local labor and employment, safety/health, or civil rights laws/regs, inferring protected characteristics and using predictive behavior analysis to make employment-related decisions. 

  • Employers may not rely solely on ADS when making disciplinary or termination decisions. Human review and corroborating evidence are required. 

  • Employees may request a description of the employee’s data used by the ADS in connection with a disciplinary or termination decision. 

  • Employers that primarily rely on ADS for these decisions must provide a prescriptive post-use notice explaining the role of the system and the employee's rights.

The law enters into effect on July 1, 2027, and enforceable by both the Labor Commissioner and public prosecutors.


California Legislature Passes Amendment to California Digital Age Assurance Act

On September 10, 2026, California passed AB 1856, which would amend the California Digital Age Assurance Act ("DAA") already set to take effect on January 1, 2027.

AB 1856 (official redline here) would make some potentially major changes.

  • Scoping changes: The definitions would be amended to somewhat limit DAA's scope. 

    • Definition of "user" deleted: The term "user" is no longer defined. Previously, it was defined as "a child that is the primary user of the device." 

    • Fewer software components are "applications": The definition of "application" now explicitly provides a software component is only an "application" if it itself is offered to consumers through a covered application store. 

      • This suggests that mods/open source software is not an "application" (see below too). 

    • Open-source systems no longer in scope: The definition of "operating system provider" now explicitly excludes OS providers like Linux and SteamOS. 

  • Substantive requirements changes: This bill would also:

    • Expand the baseline age-data-sharing requirement for operating systems to include not just covered application stores, but also "developer[s]."

    • Require covered application stores to facilitate age-data-sharing between users and developers.

    • Prohibit regulated entities from "prompt[ing] the user to change the user's age information."

    • Collection data minimization; a person may not "request a signal with respect to a particular user... from [certain regulated entities] if not required to do so by [law]."

    • Modify the standard of "actual knowledge of the age range of the user" -- e.g., by defining what is "clear and convincing information" about age range.

California Amends Insurance Information and Privacy Protection Act,

On September 27, 2026, California passed SB 354, amending the Insurance Information and Privacy Protection Act.

Entering into effect on July 1, 2028, the law provides standards for the collection, processing, and disclosure of consumers’ personal information by licensees, surplus line insurers, reinsurers, and their third-party service providers. Its requirements include:

  • Breach notification

  • Data minimization

  • Disclosure of data practices regarding consumers’ personal information through a privacy notice, including the categories of personal information that are processed or shared, the categories of sources, and the recipients of data.

  • Permitting consumers to choose whether to opt in to the sharing of their personal information by licensees, surplus line insurers, or reinsurers for purposes other than insurance transactions in certain circumstances.

  • Permitting individual consumers to request access to their personal information to verify or dispute the accuracy of the information.

  • Informing consumers of the reasons for adverse underwriting decisions.

Connecticut AG settles with TaxAct over pixel data sharing

On August 19, 2026, TaxAct agreed to pay a $275,000 fine to Connecticut to settle allegations that it improperly shared sensitive taxpayer data with Meta and Google. TaxAct also has agreed to specific compliance obligations, including creating a review committee and developing internal policies and procedures governing pixel technologies and tracking practices that include a tag monitoring system.

Connecticut AG's office investigated TaxAct's data sharing practices and alleges that it found TaxAct disclosed detailed financial information to Meta and Google for analytics and marketing purposes without appropriate contractual limitations on the ad platforms’ use of the data. The AG alleges that the data sent to Meta and Google included rounded adjusted gross income, rounded tax refunds and/or taxes owed, and certain types of income and deductions, including number of dependents and whether taxpayers made charitable contributions, or had investment income or mortgage or student loan interest.

The AG also alleged that individuals were not provided proper notice of the data sharing and instead promised to safeguard their customer's privacy and prohibit sharing of their data with third parties.


Ohio AG Leads Class Action Lawsuit Against Roblox

On August 10, 2026, the Ohio AG announced that it had filed a motion for lead-plaintiff status in a case on behalf of the Ohio Public Employees Retirement System and the State Teachers Retirement System of Ohio against Roblox.

The motion alleges that the Ohio funds have the "largest financial interest” in the relief sought by the class due to their loss of more than $21.5 million incurred from Roblox Corporation common stock. This loss was allegedly fueled by the alleged misrepresentation of the "platform as a safe space for children while failing to implement basic protections against online predators."


Washington AG Issues Privacy Report

On August 14, 2026, Washington Attorney General Nick Brown released the state’s first-ever AG Data Privacy Report. While the report carries no direct regulatory weight and creates no immediate compliance duties, it establishes the Attorney General's legislative agenda ahead of upcoming sessions.

Key recommendations from the report include:

  • Strict Data Minimization: Shifting away from standard "notice-and-choice" frameworks toward requiring explicit consumer consent for any data processing beyond what is necessary to deliver a requested service. Collection, usage, and retention limits are modeled after standards in states like California, Colorado, Connecticut, and Oregon.

  • Prohibition on Dark Patterns: Banning deceptive user interfaces that manipulate choice. Citing California Privacy Protection Agency (CPPA) guidance on choice symmetry, the report targets design patterns that pair prominent "Accept All" prompts with hidden or multi-step opt-out paths.

  • Closing Statutory Exemptions: Recommending legislative updates to narrow existing privacy exceptions, specifically extending biometric protections to cover photo, video, and audio data, while expanding precise location privacy beyond health and license plate reader applications.

  • Data Broker Transparency: Supporting statutory mechanisms like HB 2483 to require annual state registration for data brokers, mandatory security safeguards, public disclosures, and centralized deletion and opt-out mechanisms for consumers (e.g., DROP).


FTC Announces That It Will No Longer Bring Claims Based On Disparate-Impact

On August 7, 2026, the Federal Trade Commission announced a policy statement clarifying that the Commission will not pursue claims based on disparate-impact or “unfair discrimination” theories. 

The policy statement follows President Donald Trump’s issuance of an executive order last year on “Restoring Equality of Opportunity and Meritocracy” that set forth “the policy of the United States to eliminate the use of disparate-impact liability in all contexts to the maximum degree possible to avoid violating the Constitution, Federal civil rights laws, and basic American ideals.”

FTC Seeks Input on Personalized Pricing

On August 19, 2026, the FTC announced that it is seeking public comment on its enforcement policy statement regarding personalized pricing. The proposed enforcement policy addresses a number of aspects of personalized pricing–prices that are set in part based on personal data–and theories for potential liability under the FTC Act.

The policy statement notes that the FTC intends to conduct aggressive enforcement against personalized pricing practices that violate the FTC Act or other laws enforced by the Commission. The FTC further notes that, where consumers reasonably expect that prices for a product or service will not vary based on their personal data, businesses that engage in personalized pricing should clearly and conspicuously disclose that the price is personalized, the basis for the personalization, and the types of data on which it is based. It indicates that a failure to make these disclosures is likely to constitute an unfair or deceptive act or practice. It also suggests that consent may be required before personal data can be used for personalized pricing.


Wyden Letter to State Attorneys General Regarding the Use of GeoIP to Determine Whether to Honor GPC

On August 3, 2026, US Sen. Ron Wyden urged 10 state Attorneys General and the CPPA to provide clearer guidance on how businesses should honor Global Privacy Control (GPC) signals. In a recent letter, Wyden criticized the use of GeoIP to determine whether to honor a GPC signal, arguing that IP-based geolocation is often inaccurate and, even when accurate, does not determine a consumer's state residency. He also criticized the lack of transparency when businesses disregard GPC signals, noting that users are often only notified when a signal is honored.

Wyden pointed to commitments from several consent management platforms (CMPs), including OneTrust, Ketch, and TrustArc, to implement features such as residency self-certification, location correction tools, and notices when a GPC signal is disregarded. In his view, these developments demonstrate that alternatives to GeoIP-based filtering are commercially feasible. He ultimately called on regulators to issue coordinated guidance clarifying that businesses should honor GPC signals from state residents regardless of physical location, IP address, or VPN use, and to establish a bipartisan multistate AG task force focused on GPC enforcement.

If regulators follow through, the letter could signal a continued move toward more coordinated privacy enforcement, a trend already emerging through multistate privacy enforcement initiatives like the Consortium of Privacy Regulators.


White House Authorizes Vetted Private Companies to Conduct Offensive Cyber Operations Against Foreign Criminal Groups

On August 12, 2026, President Trump signed a National Security Presidential Memorandum directing the National Coordination Center to stand up a program authorizing vetted U.S. companies to conduct surveillance and disruptive cyber operations against foreign cyber-enabled transnational criminal organizations. 

Despite the "hack back" framing in press coverage, the memorandum creates no self-help right: participating companies must contract with the Department of Justice or the Department of Homeland Security, obtain written approval for each operation, and may be required to post a bond of at least $1 million, and the Computer Fraud and Abuse Act (CFAA) is unchanged. Operating procedures are due by approximately October 11, 2026.


IAPP US Data Privacy Litigation Report 2026

On August 17, 2026, IAPP has published its US Data Privacy Litigation Report for 2026. The Report covers 8 categories: 

  • Breach of contract and warranties

  • CIPA

  • Federal Wiretap Act

  • VPPA

  • CCPA's private right of action

  • Biometrics and consumer health data

  • Daniel's Law (re public officials' privacy)

  • Shareholder actions

This report analyzes the significance of private litigation and class-action lawsuits in contesting privacy violations in the U.S., tracking the trends and distilling compliance insights.


State AGs Announce $17.1 Billion Settlement with Meta

On August 26, 2026, Connecticut AG Tong announced a $17.1 billion multistate settlement with Meta Platforms, Inc. Meta must pay $12.19 billion over 10 years, which increases to the full $17.1 billion if TikTok, YouTube and Snapchat agree to comparable safety terms and monetary relief in their own enforcement actions.

In addition to monetary relief, Facebook must also implement the following safety features:

  • Robust age assurance to determine if a user is U13 or U18

  • Prohibit teen users' access to Meta's platforms from 12:00 a.m. to 6:00 a.m. by default

  • A combined 2-hour daily limit by default across Facebook and Instagram for teen users, this daily limit decreases to 1-hour if Snapchat, TikTok, and YouTube adopt comparable terms.

  • Disable notifications for teen users during school hours 

  • Implement "productive pauses" after 15 minutes of continuous use and again at 60 and 90 minutes"

  • Providing teen users with the ability to select a "non-personalized feed" as their default home feed within 4 months of the settlement's effective date.

  • Disabling teen users' ability to see the number of likes and reactions by default

  • Disabling teen users from applying cosmetic filters to their content 

The attorneys general of Alabama, Alaska, American Samoa, Arizona, Arkansas, California, Colorado, Connecticut, Delaware, District of Columbia, Georgia, Hawaii, Idaho, Illinois, Indiana, Iowa, Kansas, Kentucky, Louisiana, Maine, Maryland, Massachusetts, Michigan, Minnesota, Mississippi, Missouri, Montana, Nebraska, Nevada, New Hampshire, New Jersey, New York, North Carolina, North Dakota, Northern Mariana Islands, Ohio, Oklahoma, Oregon, Pennsylvania, Puerto Rico, Rhode Island, South Carolina, South Dakota, Tennessee, Utah, Vermont, Virginia, Washington, West Virginia, Wisconsin, and Wyoming also joined the settlement.


Sixth Circuit Grants Rehearing En Banc Regarding FCC's 2023 Data Breach Order

On July 31, 2026, the Sixth Circuit granted the petition for rehearing en banc regarding Ohio Telecom Ass'n v. FCC. The case is a consolidation of challenges brought by industry groups (Ohio Telecom Association, Texas Association of Business, CTIA, NCTA, and USTelecom) regarding the FCC's 2023 Data Breach Reporting Requirements.

The 2023 data breach requirements were issued by the FCC after an initial 2016 FCC order on privacy and data security requirements was voided by Congress pursuant to the Congressional Review Act (CRA). The previous decision, issued in 2025, upheld the FCC's 2023 data breach reporting requirements, holding that the FCC had the authority to issue the data breach rules under Section 201(b) of the Communications Act. The 2025 decision also held that the 2023 FCC rules were not barred by the rejection of the 2016 FCC order, as the 2023 rules were not "substantially the same" as the 2016 order rejected by Congress. 

The granting of the petition for rehearing vacates the previous decision and judgment of the court, the mandate is stayed, and the case is restored to the docket as a pending appeal. Argument is scheduled for October 21, 2026. 


Seventh Circuit Dismisses BIPA Claim Against Samsung Related to On-Device Processing Claims

Samsung was sued in a class action lawsuit where the plaintiff’s alleged Samsung’s photo grouping feature violated Illinois Biometric Information Privacy Act (BIPA). The district court had dismissed the claim (for failure to state a claim) and plaintiffs appealed to the Seventh Circuit Court of Appeals.  On August 7, 2026, the Seventh Circuit agreed with the lower court and dismissed plaintiffs’ claims.

The decision turned on whether Samsung was “in possession” of the biometric identifiers generated by Samsung's face grouping technology.  Samsung’s defense was that the processing occurred on device and therefore they were not “in possession” of and did not “collect, capture, or otherwise obtain” biometric identifiers or information.

“The question before us is whether Plaintiffs have sufficiently alleged that, by preinstalling the Gallery App on its devices and allowing its use, Samsung (1) is “in possession of” Plaintiffs’ biometric data as that phrase appears in BIPA § 15(a) or (2) “collect[ed],” “capture[d],” “or otherwise obtain[ed]” Plaintiffs’ biometric data within the meaning of BIPA § 15(b). 740 Ill. Comp. Stat. 14/15(a), (b).2”

In its analysis, the court reviewed  the “ordinary and popular” meanings of these terms and concluded:

“From these Illinois decisions, we too conclude that the words “possession,” “collect,” “capture,” and “obtain,” as they appear in BIPA § 15(a) and (b), all require the subject company to have or have obtained some degree of “control” over the biometric data in question…Although Plaintiffs describe how Samsung provided users with the products (the phones and tablets) and software (the App) to record, create, and save facial bio metric data on the individual devices, they allege nothing from which we can reasonably infer that Samsung itself controlled the data…For their part, Plaintiffs point out that the Gallery App gives users the ability to back up their photos to Samsung’s cloud servers. From this, they argue, one could reasonably infer that the associated facial geometry data (like the photographs themselves) are also backed up to Samsung’s cloud servers. But this is not necessarily so, and Plaintiffs do not provide any plausible support for this theory.”


California Legislature Sends Pixel-Related CIPA Reform Bill to Governor

On September 12, 2026, California’s SB 690 became law without veto, narrowing the private right of action in California’s wiretap law (“CIPA”), effective January 1, 2027. Specifically, this amendment would somewhat restrict the private right of action in California’s wiretap law (“CIPA”), effective January 1, 2027. Specifically, this amendment would:

  • Partially remove CIPA’s private right of action, so that alleged violations of Cal. Pen. Code sec. 638.51 arising from conduct “occurring on an internet website, online application, or mobile application” could be prosecuted only by the California AG. 

  • Negate “any [such private,] pending claim in an action commenced [on or after January 1, 2025]”

SB 690 is a direct response to the rise in CIPA lawsuits based on allegedly unlawful use of pixels and other tracking technologies online, especially coming from plaintiff-bar attorneys - though many such lawsuits allege unaffected CIPA provisions. If enacted, this amendment will somewhat decrease the volume of pixel-related lawsuits.

However, SB 690 would likely also result in additional privacy-related complaints going to the California AG, increasing the risks of high-profile, high-consequence investigations. Additionally, it leaves the private right of action intact for claims under the wiretapping (§ 631), eavesdropping (§ 632), and recording (§ 632.7) provisions. Plaintiffs are likely to shift lawsuits to those later provisions.  


CalPrivacy DELETE Act Enforcement Advisory

On September 3, 2026, CalPrivacy issued Enforcement Advisory 2026-01, highlighting data brokers who provide incorrect information in their annual registration with California’s data broker registry.

From the press release: “CalPrivacy has issued Enforcement Advisory 2026-01highlighting data brokers who provide incorrect information in their annual registration with California’s data broker registry. The advisory stresses that data brokers are liable to pay a fine for each day incorrect information appears in the registry, observing that the Enforcement Division has brought multiple enforcement actions over reporting errors.[*] … If consumers think a business provided incorrect information with its data broker registration, they should report it via the agency’s complaint form.”


Governor Vetoes Amendment to CCPA Limiting Disclosures of Sensitive Data

On September 27, 2026, California's governor vetoed AB 1542, which would have amended CCPA to prohibit businesses, service providers, and contractors from "selling"/"sharing" sensitive personal information to third parties, with exceptions for specific disclosures.

The governor’s letter cited concerns with a categorical ban on such disclosures and potential unforeseen implementation and enforcement costs.


CT AG investigating MediaLab.AI's Kik app for unfair, deceptive practices, privacy law violations

On September 8, 2026, Connecticut's AG announced that his office has sent a civil investigative demand (CID) for information about MediaLab. AI's Kik app. The CID includes requests for details related to data processing, content moderation, and age assurance practices. In the press release, the AG describes the app as popular with minors for sharing texts, private chats, photos, and videos and calls the Kik app a "predator's paradise."

“Kik is a parent’s worst nightmare—a cesspool of sexual abuse, exploitation and bullying, with no meaningful age verification or barriers or protections.” said Attorney General Tong. “Our investigation demands detailed answers from MediaLab regarding their unacceptable record on child safety and privacy. We just forced Meta to overhaul its platform and pay $17.1 billion for hurting our kids, and we’ve put TikTok, YouTube and Snap on notice. Our investigation into Roblox is active and ongoing. One by one, we are taking on these toxic apps and we are going to use the full weight of our law enforcement authority to hold Big Tech accountable and protect our kids online.”


CT AG Reminds Consumers of Privacy Rights Entering into Effect

On September 16, 2026, the Connecticut AG published a reminder that, under amendments entering into effect on October 1, 2026, additional privacy rights, "related to artificial intelligence, Facial Recognition Technology (FRT), genetic data privacy, surveillance pricing, and data brokers, as well as through recent amendments to the Connecticut Data Privacy Act (“CTDPA”)” are entering into effect.

Under SB4, the AG highlighted the following rights and requirements:

  • Limitations on surveillance pricing as well as disclosure requirements for businesses using personal data in price setting;

  • Limitations on and disclosure requirements for the use of FRT, including requiring that companies post clearly legible signage alerting consumers that FRT is in use on the premises and providing them with a conspicuous hyperlink or quick response code directing them to the company’s facial recognition technology policy;

  • Limitations and consent obligations for Direct-to-Consumer Testing Companies that are collecting consumer’s genetic data, including providing consumers with a property right and exclusive control over the collection, use, retention, maintenance, disclosure, and destruction of the sample and result;

  • Further limitations on what is considered publicly available information as well as expanded consumer data deletion rights related to consumer profiles generated from publicly available information;

  • A ban on the sale of consumer’s precise geolocation data; and

  • The creation of a data broker registry which requires data brokers to register with the Connecticut Department of Consumer Protection by January 1, 2027.

Under SB5, the AG highlighted the Connecticut Artificial Intelligence Responsibility and Transparency Act (“CART Act”) with the following rights and requirements:

Chatbots and Kids

o   Companies that offer chatbots to children must put a protocol in place to detect and address chats indicating a risk of self-harm;

o   Chatbot platforms must offer parental controls;

o   Chatbots are prohibited from sending harmful communications to children;

o   Chatbots cannot encourage children towards physical violence, substance abuse, or disordered eating; and

o   Companies that offer chatbots to children cannot allow their chatbots to engage in romantic or sexual interactions with children or use manipulative engagement mechanics to keep them using the platform.

AI and Employment

o   Employers must provide written notice when using AI to make a decision that impacts terms, privileges, or conditions of employment; and

o   Employers are prohibited from using AI to discriminate against employees, and any such discrimination is considered employment discrimination that is also violative of the Connecticut Fair Employment Practices Act.


New Biometric Law for Erie County, NY

In April 2026, Erie County, NY passed a law banning the collection, use, and sale of biometric identifiers in commercial settings.

Businesses that previously collected biometric data are obligated to notify Erie County Division of Consumer Protection (within 30 days of the law's effective date) and destroy the biometric data in a secure manner. Penalties include up to $5,000 per day for violations left uncured after the 30-day cure period. The law became effective on June 5, 2026.


Delaware Enacts Major Amendments to Its Privacy and Breach Notification Laws

On September 2, 2026, Delaware enacted HB 380 and HB 381. HB 380 substantially amends the Delaware Personal Data Privacy Act (DPDPA); HB 381 amends Chapter 12B, Subtitle II, Title 6 of the Delaware Code, the state's computer security breach statute.

HB 380 broadens the DPDPA considerably, with the following expansions in scope:

  • The applicability threshold drops from 35,000 to 10,000 consumers (or 5,000 where more than 20% of gross revenue comes from selling personal data).

  • Third parties that acquire personal data from a controller are now in scope and carry standalone duties under a new § 12D-107A.

  • "Sensitive data" expands to reach national origin, health treatment or status, neural data, financial account information, government identifiers, and inferences drawn from any of these.

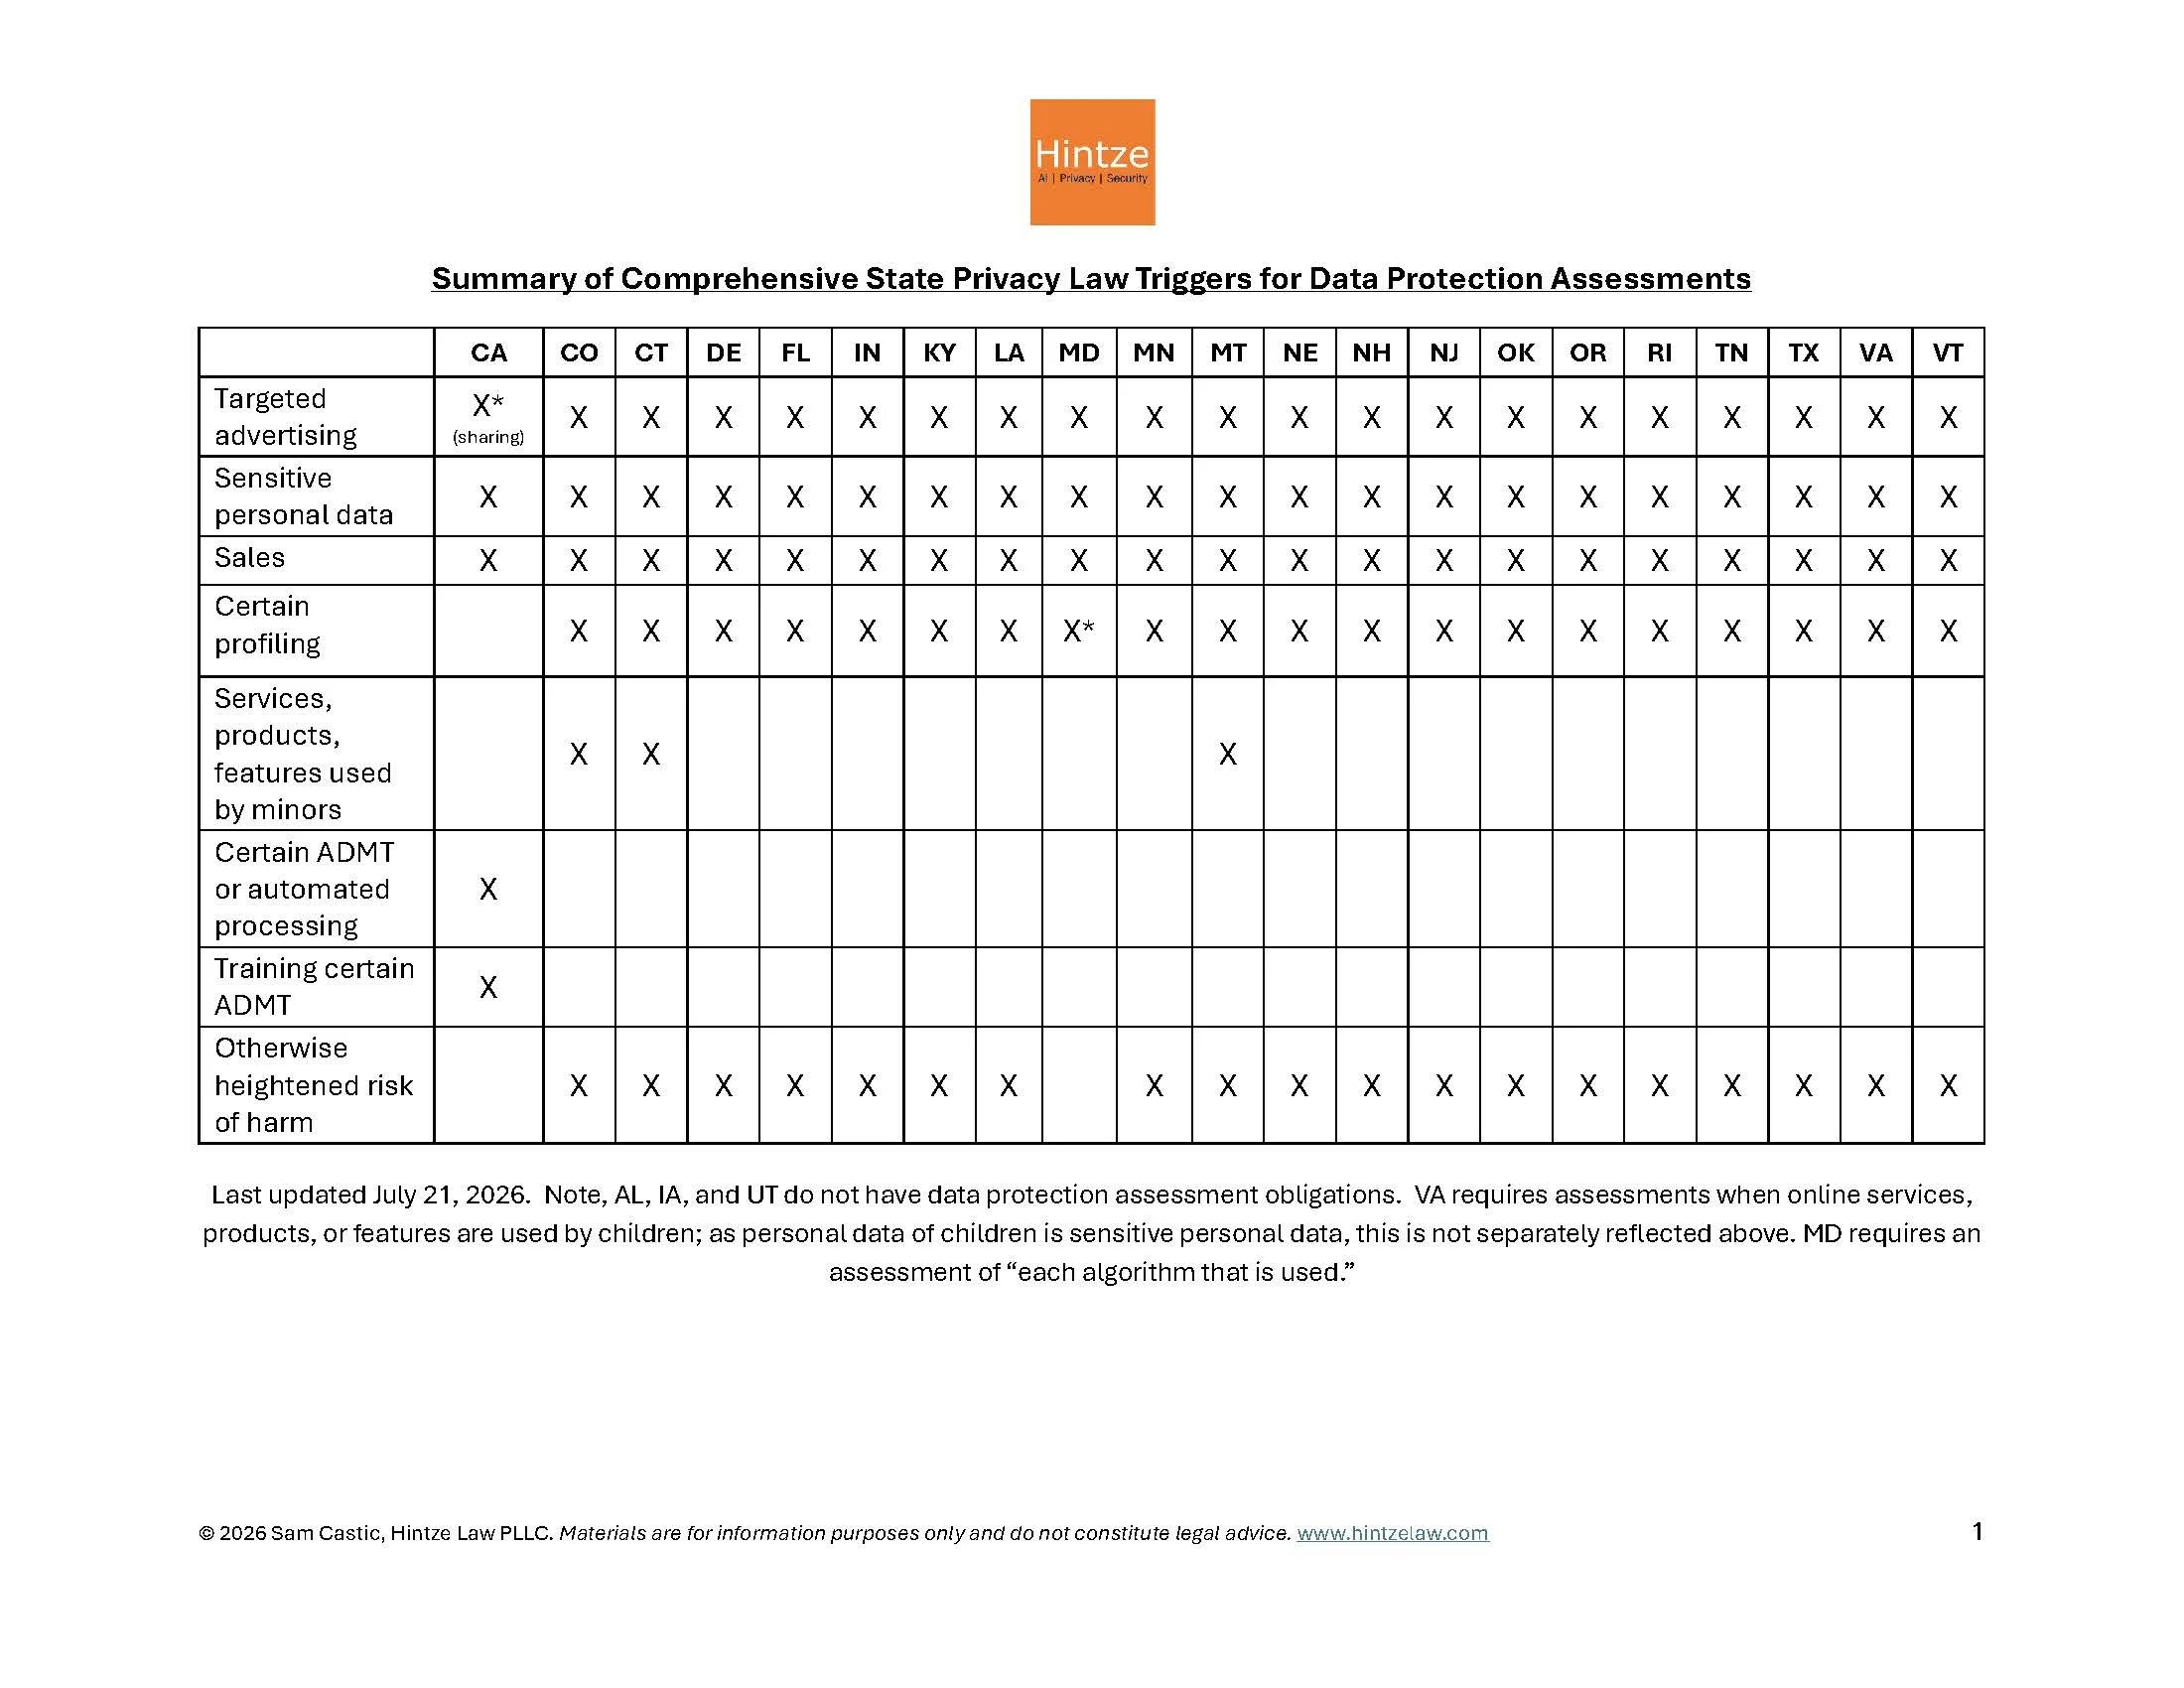
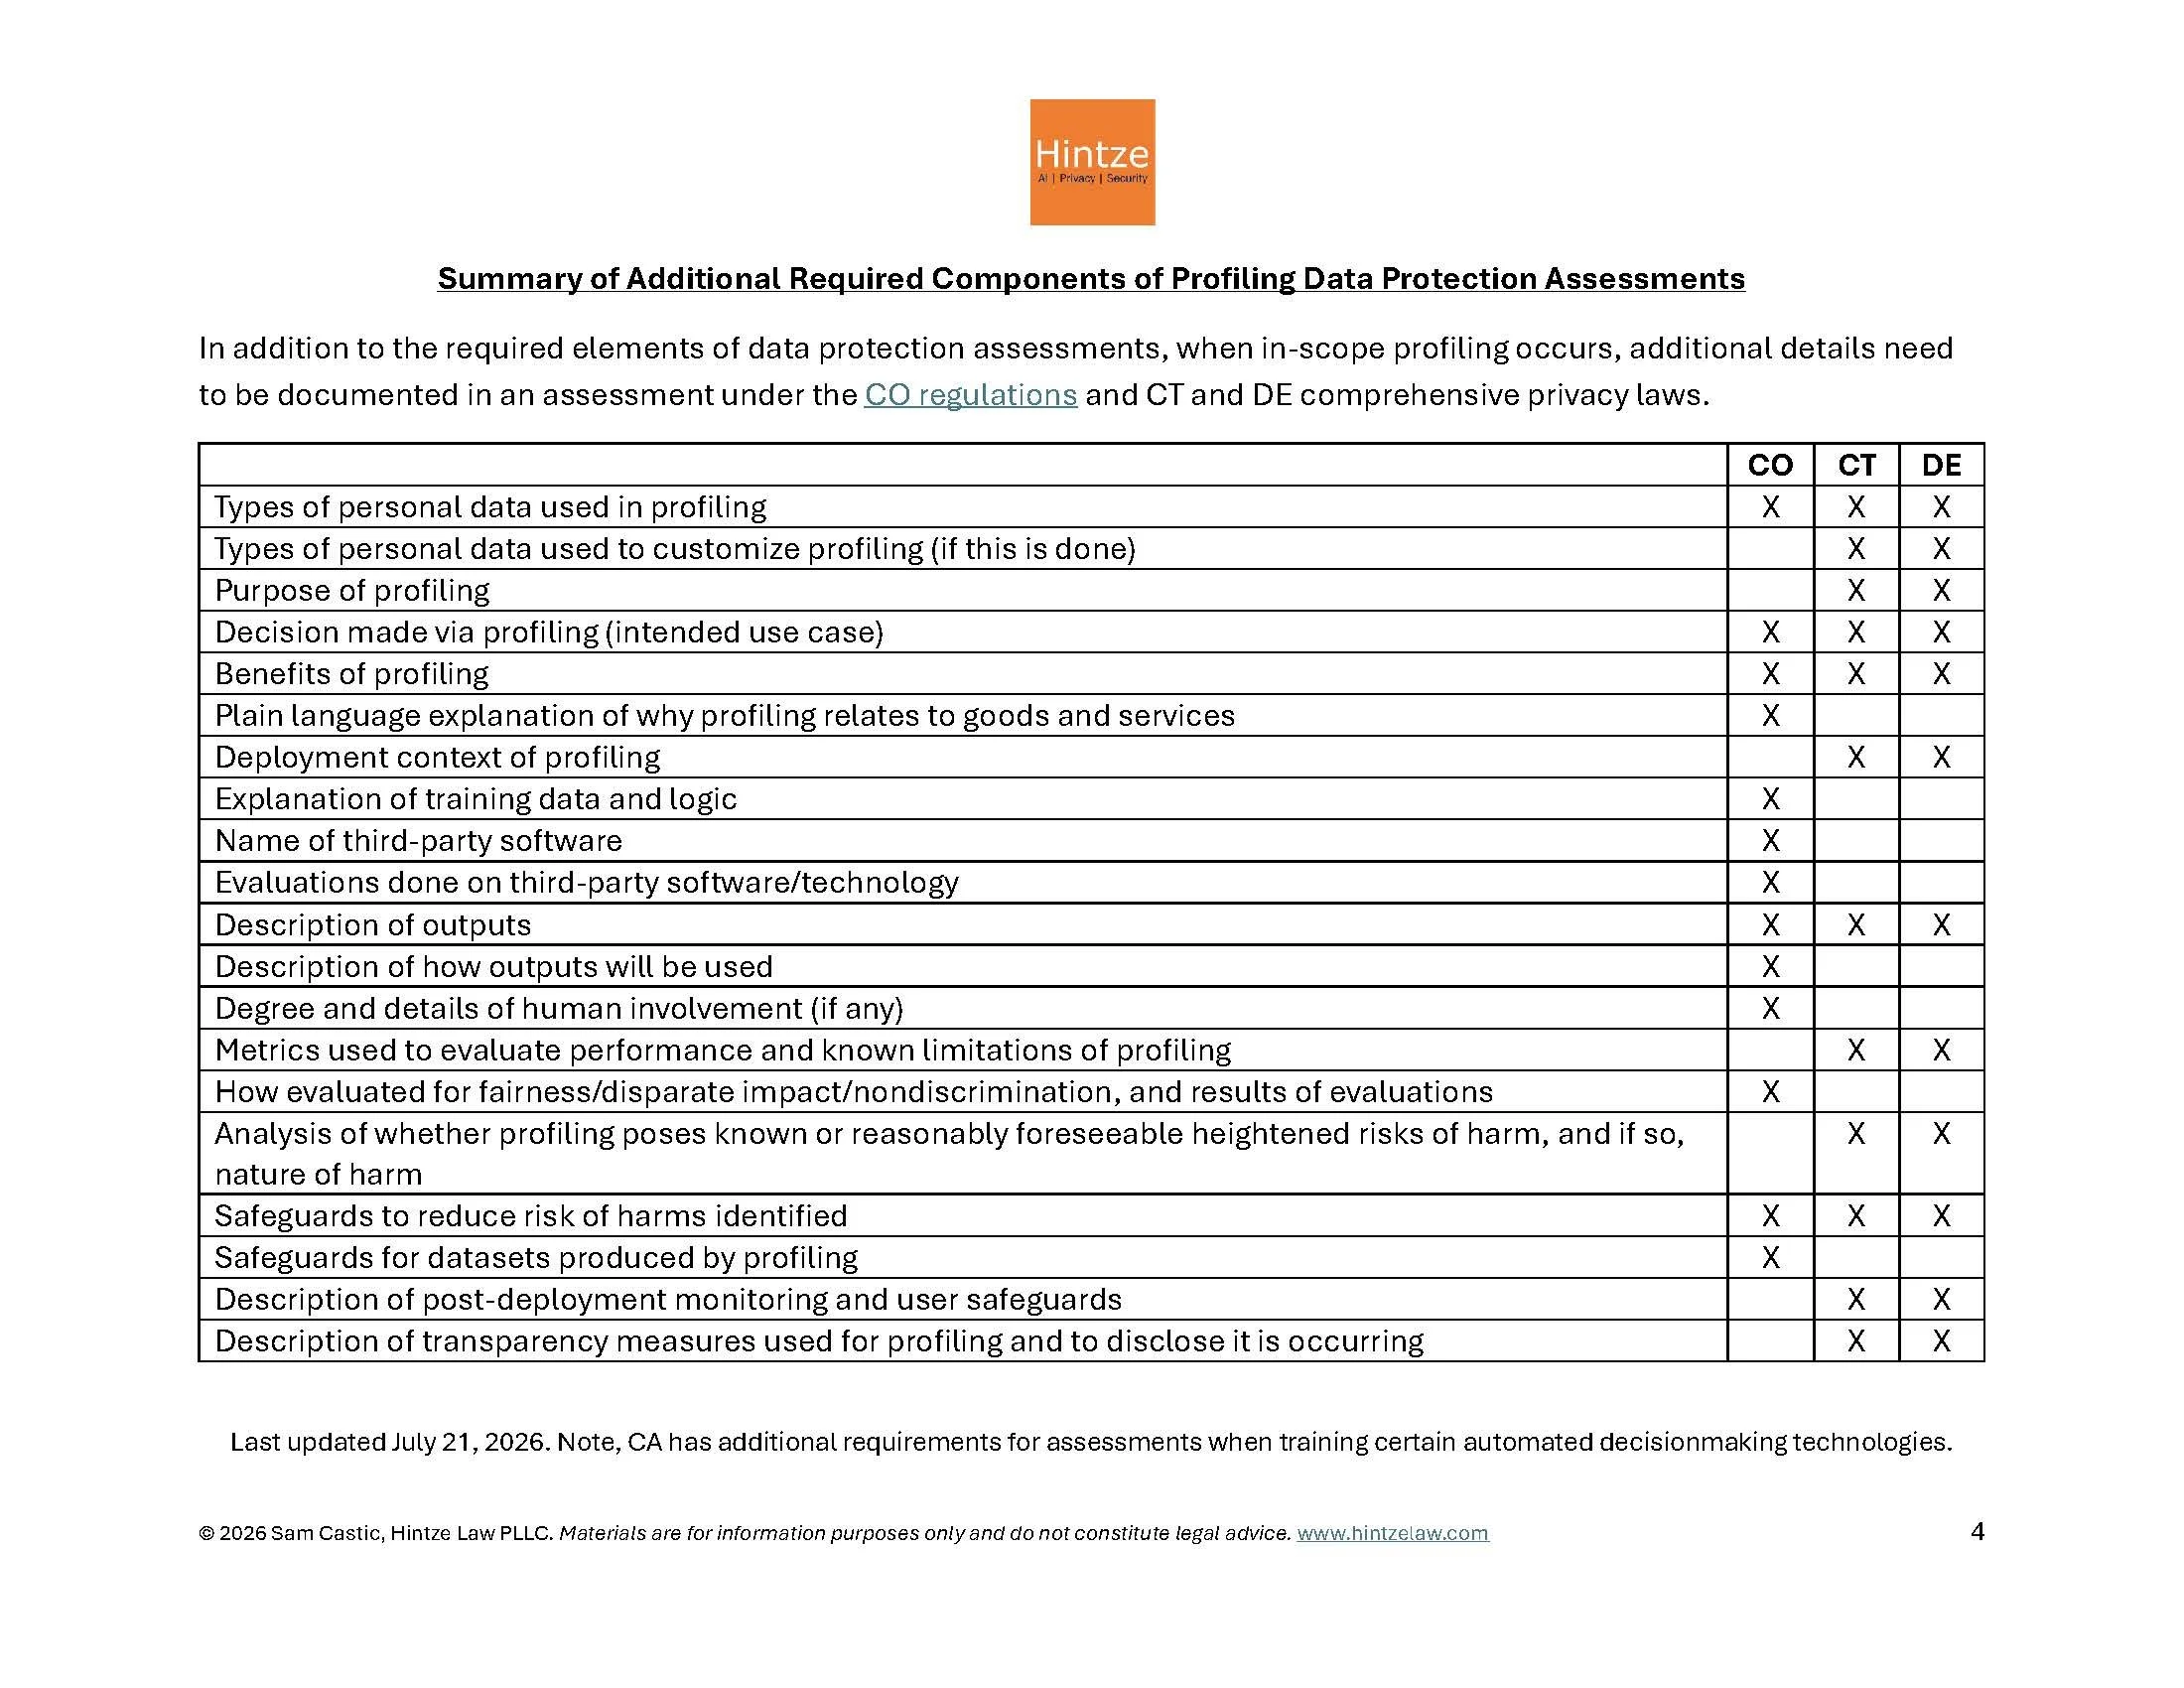
  • The data protection assessment threshold falls from 100,000 to 50,000 consumers, and profiling that feeds automated decisions with legal or similarly significant effects now requires a separate documented impact assessment.

  • HB 380 also eliminates the entity-level Gramm-Leach-Bliley Act (GLBA) exemption and replaces it with narrower carve-outs for insurers, chartered banks, credit unions and savings associations engaged in financial activities as described in the GLBA, and registered securities firms.

  • HB 380 does not exempt employment data across the board, so personal data in the employment-context loses its exemption for profiling and generating reports in connection with decisions that produce legal or similarly significant effects.

HB 380 introduces new obligations as well:

  • Sensitive data may not be disclosed in a sale unless: strictly necessary to provide a product or service the consumer requested; clear and conspicuous notice identifying the specific categories, purpose, and recipients; consumer consent; and a consent record retained five years.

  • Controllers disclosing a report for use in a decision producing legal or similarly significant effects must provide adverse action notice, an explanation of the data relied on, and an option for human review — a Fair Credit Reporting Act-style overlay on the privacy law.

  • Controllers must conduct documented due diligence on third-party recipients of personal data and enter contracts with those recipients with specified terms.


HB 381 requires AG notice within 60 days where affected residents cannot be identified within that window, folds AG notice and social media publication into substitute notice, and narrows the safe harbor for HIPAA- and GLBA-regulated entities so that following a regulator's breach procedures satisfies only the 60-day timing rule rather than the whole chapter.

Organizations should reassess their DPDPA applicability against the lower thresholds, inventory sensitive data including inferences, build consent capture and five-year retention for any sensitive-data sale, map third-party data flows and reevaluate third-party due diligence and contract requirements, and assess AI hiring and workforce tools, which lose the employment-data exemption when used for profiling or shared with third-party decision vendors. Incident response teams should revisit their response plans for compliance with the updated 60-day notice deadline.


FTC Rescinds 2021 Policy Statement on Health App and Connected Devices Breaches

On September 9, 2026, the FTC announced that it had rescinded the 2021 Policy Statement on Breaches by Health Apps and Other Connected Devices, citing that the 2024 update to the Health Breach Notification Rule rendered it unnecessary and in accordance with President Trump's directive to agencies to eliminate unnecessary rules and obsolete guidance.


Louisiana AG Sues Snap and Discord

On August 27, 2026, the Louisiana Attorney General announced a lawsuit against Snap, Inc. and Discord. The suits allege violations of the Louisiana Unfair Trade Practices Act (LUTPA), negligence and public nuisance, and unjust enrichment. The alleged violations are centered around harm to minors on the platforms while the platforms marketed themselves as safe for children. The suits are also seeking a TRO and preliminary injunction to prohibit engaging in any activity in violation of LUTPA, representing that the platforms have adequate safety features, and failing to implement reasonable measures designed to protect minors from harm.


Texas Judge Grants Partial Summary Judgment Against TikTok

On September 10, 2026, the Texas AG announced that its motion for partial summary judgment against TikTok had been granted. The District Court held that Texas met its burden to establish that:

1.       TikTok's claim that it would remove video content that violated its Community Guidelines, but instead categorizing it as "hard to find" violated the Texas Deceptive Trade Practices Act; and

2.      "Restricted Mode [i.e., the mode designated for minors] was not functioning in the way it was marketed and exposed users to a high volume of content that should have been filtered out."

The trial against TikTok for relief and penalties is expected to be set for next month.


City of Seattle Bans Surveillance Pricing in Grocery Stores

On September 22, 2026, the Seattle City Council passed the Fair Pricing and Transparency Ordinance banning the use of algorithmic pricing in grocery stores. nThe ordinance also requires mandatory disclosures of pricing and discounts. It now heads to Mayor Wilson's desk for signature.

"Covered retailers" are defined as a delivery service provider, a mixed-use grocery business, or a grocery business that has 20 or more retail locations globally, including but not limited to chains and integrated enterprises. "Delivery service provider" is defined as an organization that employes 100+ employees worldwide and facilitates delivery or online ordering services from a grocery business, mixed-use grocery business, or warehouse to a consumer in Seattle, regardless of where the business is located. Specifically exempted are convenience stores, food marts, and farmer's markets.


NYDFS Guidance on Cybersecurity Risk Assessments

On September 10, 2026, the NY Department of Financial Services issued Guidance on How to Conduct and Use Risk Assessments Required by the DFS Cybersecurity Regulation to the entities covered under the Banking Law, the Insurance Law or the Financial Services Law. The guidance clarifies the existing requirements under the Cybersecurity Regulation (23 NYCRR Part 500) following the Department’s review of common gaps in risk assessments.

The guidance highlights the following requirements for more dynamic, data-driven assessments which are integrated into broader enterprise governance processes:

  • Covered Entities must designate a Chief Information Security Officer (“CISO”) or a Senior Officer to oversee the Risk Assessment process and must ensure that the results of risk assessments are communicated to senior management.

  • While a specific methodology is not required, Covered Entities are recommended to adopt “a clear and repeatable methodology for identifying, analyzing, and prioritizing actions to address cybersecurity-related risks” and to periodically review the methodology for appropriateness for their organization.

  • Covered entities should consider the full range of internal and external factors that could affect their cybersecurity risk profile, including emerging risks, third-party and supply chain risk, and cyber interdependency and concentration risk. The department notes that entities are “required to maintain an accurate and current asset inventory.”

  • Covered Entities must retain documents showing “how cybersecurity risks were identified, assessed, and addressed through the Risk Assessment process,” including evidence and reasoning support conclusions and decisions.

  • Covered Entities should track risks and remediations over time for better visibility into the status of identified risks over time.

  • Covered Entities should integrate risk assessments into broader cybersecurity programs and update them at least annually or whenever there is a material change to their risk.


Global Updates


Apple to Change Language of Consent Management Pop-ups in the EU

On August 17, 2026, an investigation by Germany's Federal Cartel Office found Apple's consent management phrasing in its App Tracking Transparency framework steers users away from data sharing with third party-developers but had more favorable consent prompts for its own apps. Apple has four months to implement the changes. 


Brazil's ANPD Announces Investigation into Discord

On August 7, 2026, Brazil's data protection authority, the ANPD, announced that it has launched an investigation into Discord. The investigation focuses on Discord's possible failures in implementing measures required by the ECA Digital Act, including the absence of age verification measures, failures to remove violating content, and failure to make required regulatory reports. Discord had five business days to present information on existing mechanisms for compliance with the ECA Digital. 


Brazil's ANPD Fines TikTok $153.7 million real for failures in protecting children's and teen's data

On August 25, 2026, the Brazilian ANPD issued a fine to ByteDance for violations of the LGDP. The sanction includes the $153 million fine and the requirement to delete the data collected irregularly. The violations were identified both in access to TikTok without account registration and with account registration, and in both instances the data of children and teens were being processed without adequate legal basis. In response to the ANPD sanctions, ByteDance has committed to implementing a compliance plan to improve the protection of children and teens on TikTok. 


Dutch DPA fined Uber $966M for automated driver suspensions that violated GDPR

On August 21, 2026, the Dutch privacy regulator fined Uber $966m for allegedly automating driver suspensions, with no warning or human involvement. Uber allegedly violated driver’s rights not to be subject to automated decision-making that has significant consequences and the right to be informed.


Indian High Court Recognizes Right to be Forgotten

On July 27, 2026, the High Court of Karnataka issued an order in Writ Petition No. 22456 of 2025. The petitioner requested the search engine deindexing of court records following her 2019 acquittal, which the court granted, holding that Article 21 of the Constitution grants a right to be forgotten.


Australian Privacy Law Reforms Proposed

On August 31, 2026, Australia published its initial proposals for the second wave of Privacy Act reforms.  Proposed updates include an expanded definition of personal information, a new “fair and reasonable” test, new “trading” prohibition, simplified collection and notice requirements, updated breach notification requirements, right to erasure, and controller-processor distinctions. Feedback on the proposal is due by September 18, 2026. Legislation containing these proposals is likely to be introduced before the end of the year.

Discord Implements Youth Safety Measures Globally

On September 23, 2026, Discord implemented its age assurance and youth protections globally, publishing an accompanying blog post and placing users as Teens, Adults, or Unconfirmed. Discord internally estimates user age by connected communities, servers, and games; general activity levels, and account history and age.

Following backlash to Discord's use of Persona for its ties to Peter Thiel, Discord shifted to k-ID for Facial Age Estimation and ID document scan + selfie and now also provides age checking through credit card check, AgeKey, Google Wallet, and the Apple/Google Play Store. The safety page also discloses how each method works, what data is involved, and what's retained by whom.

The blog summarize the protections for teen accounts, including restrictions on messages from unfriended users, content filtering, and restrictions on profile details--all enabled by default and the first two only able to be adjusted by a confirmed adult.

As industry best practices for age assurance developed, businesses should be aware of methods and safeguards implemented by firms such as Discord and Roblox and determine whether those practices are appropriate for their risk profiles.


EDPB Announces Guidelines on Administrative Fines

On September 21, 2026, the EDPB announced that it adopted guidelines on the application of the power to impose administrative fines, replacing the WP29 guidelines on the application and setting of administrative fines and complement the previously adopted guidelines, The press release provides a 5-step methodology:

1.      "The DPA checks if the infringement can lead to a fine, by finding support either directly in the GDPR or in national law.

2.      The DPA determines whether the party under investigation may be fined for the infringement in question. Whether the controller or the processor is liable depends on who is bound by the breached provision.

3.      The DPA assesses whether the infringement has been committed intentionally or negligently, since a culpable infringement is a condition for the imposition of a fine.

4.      The DPA assesses possible aggravating and mitigating factors. If the infringement is minor, there will generally be no fine and a reprimand may be issued instead; if it is not minor, there is a strong presumption that a fine should be imposed.

5.      The DPA assesses whether imposing an administrative fine would be effective, proportionate and dissuasive. In doing so, the DPA may consider whether, in the specific case, there is a reason to deviate from the standard approach."

The EDPB also announced it had adopted the final version of its guidelines on the interplay between the Digital Services Act (DSA) and the GDPR, following public consultation.


Netherlands Makes Publication of Data Protection Sanctions a Statutory Default

Effective September 1, 2026, GDPR sanctions by Netherlands Autoriteit Persoonsgegevens (AP) are required to be publicly disclosed. The Netherlands enacted the Verzamelwet gegevensbescherming (Data Protection Omnibus Act) on June 10, 2026 (Stb. 2026, 154), amending the Uitvoeringswet AVG, the Dutch General Data Protection Regulation (GDPR) implementing statute.

The Autoriteit Persoonsgegevens (AP) already published sanction decisions, but did so under its own disclosure policy. The amendment converts that practice into a legal obligation covering fines, orders subject to a penalty payment, and processing bans. The AP has said it will apply the same approach to sanctions under the Dutch police data and judicial data statutes.


EU Cyber Resilience Act Vulnerability and Incident Reporting Began in Effect

EU Cyber Resilience Act (CRA) was adopted on October 23, 2024 and entered into force on December 10, 2024. Its Article 14 reporting obligations became effective September 11, 2026, ahead of the Regulation's general application date of December 11, 2027.

Manufacturers of products with digital elements must report actively exploited vulnerabilities and severe incidents on a timeline: an early warning within 24 hours of becoming aware, a detailed notification within 72 hours, and a final report within 14 days of a corrective measure being available for vulnerabilities or within one month of the 72-hour report for incidents. Reports go to the Computer Security Incident Response Team (CSIRT) coordinator in the member state of main establishment, defined as where product cybersecurity decisions are predominantly taken, and reach the EU Agency for Cybersecurity (ENISA) simultaneously.

Two points are worth noting. Although Article 69(2) grandfathers products placed on the market before December 11, 2027, from most CRA requirements, Article 69(3) expressly excludes Article 14 from that exemption. The reporting duty therefore applies to the entire supported catalogue, not just current product lines. Second, ENISA's Single Reporting Platform is the sole permitted channel, with no email or national portal alternative; ENISA's platform FAQ states that at launch it will accept only mandatory reports under Article 14 and under Article 24, which covers open-source software stewards. Voluntary reporting under Article 15 is not available initially.

Organizations should confirm which CSIRT coordinates for their main establishment, identify who holds the 24-hour clock, and check that vulnerability intake covers legacy products still supported.


European Commission Unveils EU Kids Act

On September 17, 2026, the European Commission published more information about the proposed EU Kids Act, which will be organized around four pillars:

  • Social media delay: ban under 13, parental account creation control for 13-14, 15+ can create own accounts but other safety measures apply

  • Safety-by-design: feature restrictions on addictive features, harmful content, AI chatbots, and online chat/profile capabilities

  • Privacy-preserving age assurance: age verification for both new and existing users once rules go into force

  • Effective enforcement: burden of proof on very large online platforms to demonstrate services are "safe by design" with an ex-ante report, 90-day fast track investigations

The proposal will now go to the EU Parliament and Council for review and launch of the legislative process.


Irish DPC Fines Google 403 Million Euro Over Location Data

On September 21, 2026, the Irish Data Protection Commission fined Google €403 million following its inquiry into Google’s processing of location data in “Web & App Activity”, “Location History” and “Location Accuracy” between May 25, 2018 and February 4, 2020.Data Protection Commission fines Google €403 million following Inquiry into Google’s processing of l…

The decision found that Google had infringed the GDPR regarding:

  • “The lawfulness and fairness of its processing of location data in Web & App Activity and Location History,

  • Its accountability obligations under the GDPR by failing to be able to demonstrate compliance with the lawfulness, fairness and transparency principle regarding its processing of personal data in Location Accuracy;

  • Its transparency obligations in respect of all three features referred to above; and

  • Its retention of location data in Web & App Activity and Location History.”


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

New Podcast Episode: How UK and EU Cookie Practices Need to Adapt for the U.S.

For businesses operating across the U.S., UK, and EU, cookie and tracking technology compliance is becoming increasingly complex. While organizations in Europe are accustomed to consent-based requirements for nonessential cookies and trackers, the U.S. presents a different mix of regulatory requirements and litigation risk.

In Episode 2 of Data Across the Pond, Hintze Law’s Sam Castic and Skyscanner Deputy General Counsel Gemma Witham discuss how common UK and EU approaches to cookies may need to adapt for the United States. They discuss the growing trend of businesses facing legal demands and litigation due to use common tracking technologies under laws such as the California Invasion of Privacy Act (CIPA). They also discuss the types of obligations state privacy laws impose around the sale and sharing of personal data, targeted advertising, and for opt-out signals such as the Global Privacy Control (GPC).

UK and EU Cookie Compliance May Not Translate Across Borders

European organizations commonly classify cookies by categories such as strictly necessary, performance, functional, or advertising. Those categories do not align with how tracking technologies are treated under U.S. privacy laws or the legal theories driving U.S. tracking litigation.

This creates practical decisions for global businesses. Requiring consent before tracking technologies fire may help address certain U.S. litigation risks, but it may also reduces the data businesses can get from website visitors. The podcast discusses these challenges and how to think of scaling a compliance approach globally.

A Global Approach to Tracking Technologies

The conversation covers the types of capabilities and considerations companies should think of when setting a global approach to governing tracking technologies.  Gemma and Sam discuss capabilities for consents and opt-outs, up-to-date disclosures, and classifying cookies and trackers over time. 

Ultimately, the episode highlights an important distinction for global businesses: cookie compliance cannot necessarily be approached the same way on both sides of the Atlantic. Understanding the different sources of U.S. risk, and developing a tracking governance strategy that takes them into account, is an important way for cookie and tracking practices to scale globally.

Listen to the full episode here: Apple, Spotify, or YouTube


Sam Castic is a Partner with Hintze Law, chair of the firm’s Retail Group, and co-chair of the Cybersecurity and Breach Response Group and FinTech + Financial Services Group. As a former chief privacy officer, he helps companies build, scale, and right-size privacy programs and strategies.


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

California AB 1159: New Student Privacy, AI Training, and EdTech Compliance Requirements

California enacted AB 1159 on September 10, 2026. The law substantially expands student privacy obligations for education technology providers providing services to early learners, K-12, and higher-education students. It amends the K-12 Pupil Online Personal Information Protection Act  (KOPIPA), and Early Learning Personal Information Protection Act (ELIPA). It also creates the Higher Education Student Information Protection Act (HESIPA), to be codified beginning at Cal. Bus. & Prof. Code § 22587, covering operators of qualifying online services used for higher-education purposes. The law also creates a private right of action for students and their parents or guardians against operators and other covered entities. 

Reflecting a growing concern about how educational technology platforms use student data, AB1159 expands the scope of existing laws to cover not only operators but also their downstream subcontractors / service providers and adds specific restrictions on use of student data for AI training and development. AB 1159 also adds new data retention, deletion, and deidentification requirements that will increase operational and technical complexity for many edtech companies. The new early learning and K-12 requirements take effect January 1, 2027. HESIPA takes effect July 1, 2027.  

Key Changes in More Detail 

AB 1159 makes several significant changes to KOPIPA and ELPIPA.  Most changes to KOPIPA and ELPIPA are substantially similar, and the new HESIPA is largely similar to both KOPIPA and ELPIPA: 

Expanded Scope. AB 1159 covers not only an operator, but also any entity working on its behalf. The trigger for what services is also expanded. The law previously covered operators with actual knowledge its service is primarily used for school purposes and whose service was designed and marketed for those purposes.” The law expands the scope of covered services by removing the qualifier “primarily” to include any service used for school purposes and by replacing “designed and marketed” with “designed or marketed.” As a result, mixed-use and general-audience services may be covered where the operator knows the service may be used for any school purposes and if the service is either designed or marketed for that use. 

Restrictions on AI Training and Development. The other significant change under these laws is that covered student data cannot be used to train a generative AI system or service or develop an AI system. "Train” is defined broadly to include model development, model testing, and fine-tuning. 

There is an exception to those and other restrictions in this section allowing "operator's use of information for maintaining, developing, improving, or diagnosing the operator’s site, service, or application." The scope of this exception is unclear.   

A narrow reading of this exception could permit the development of AI systems incorporated into a school-facing service, but not the training of generative AI models. By contrast, a broader reading could permit the training of generative AI models offered as part of a school service, so long as the training is limited to developing or improving that service. 

While the statutory language is contradictory and, at best, unclear, interpreting it to categorically prohibit edtech providers from using student data to improve AI functionality that a school has authorized as part of a service could have significant consequences. Such an interpretation could limit California schools’ ability to use AI to operate more efficiently and restrict providers’ ability to improve the performance and safety of AI tools that schools make available to students, including tools used to educate students on the appropriate use of AI. 

Restrictions on Sensitive Information Collection. AB 1159 specifically restricts an operator’s collection, use, and disclosure of covered information concerning a student’s reproductive or sexual health, immigration status, sexual orientation, or gender identity, subject to the statute’s express terms and exceptions. 

Unlike KOPIPA and ELPIPA, HESIPA adds precise geolocation information to its list of prohibited categories of sensitive information. The enacted text does not explain why that category appears only in HESIPA. As with the AI restrictions, there is a broad exception to these restrictions for an operator’s use of information for maintaining, developing, supporting, improving, or diagnosing the operator’s service that arguably allows for some limited use. 

Deidentification Standards and School or LEA Requirements. AB 1159 builds on existing laws’ deidentification exceptions and related requirements for proper deidentification by giving schools and local educational agencies (LEAs) a role in determining whether an operator’s deidentification process is sufficient. Operators must make their deidentification processes available for review by the applicable school or LEA before using deidentified data. Schools and LEAs are not required to conduct a review, but if they do, the operator cannot treat the applicable data as deidentified unless the school or LEA determines that the process is sufficient. Where a school or LEA maintains its own deidentification policy or standard, the operator must follow that policy or standard. 

Written Retention Policies and School or LEA Retention Limits. A written data retention policy will need to be maintained and implemented, and provided to students, their parents or guardians, and school personnel upon request. The policy must describe why covered information is collected and retained, and the timeframe for deletion. AB 1159 will also require operators to not exceed a school or LEA’s retention period for the same information.  

Unlike with deidentification processes, the law does not require an operator to make its retention policy available to schools or LEAs for review prior to processing. As a practical matter, operators should be prepared to follow applicable retention schedules that schools and LEAs provide through DPAs or other vendor requirements and to configure retention periods accordingly. 

Deletion and Access Rights. AB 1159 continues to allow operators to comply with deletion and access requirements under FERPA and CCPA. The law also continues to allow students to download, export, save or maintain their own personally created data or documents.  

AB 1159 creates new deletion and access rights to address a narrow set of student information that is subject to exceptions from the CCPA’s deletion and access requirements. For deletion, these include student’s grades, educational scores, or educational test results that the operator holds on behalf of a LEA. For access, these include certain educational standardized assessment information. Once a student has been unenrolled from the LEA for at least 60 days, a parent, guardian, education rights holder, or the former student, if 18 or older, may request deletion or disclosure to the student of such information which the operator must honor, subject to more limited exceptions. Before deleting the information, the operator must obtain documentation that the student is no longer enrolled in the LEA. 

Fines and Enforcement 

AB 1159 creates a new private right of action. A student, or their parent or other guardian, will be able to sue individually or on behalf of a class to recover the greater of actual damages or $500 per plaintiff, per violation, plus injunctive relief, punitive damages, and attorney's fees. The law also provides a notice-and-cure period, giving operators 60 days after receiving written notice to correct an alleged violation before a private suit can be brought.  

Class claims require the operator to identify or reasonably attempt to identify similarly situated students, notify them that a remedy is available upon request, provide or agree to provide the requested remedy, and stop the violation. Plaintiffs must also furnish a copy of the complaint to the Attorney General within 10 days of filing. 

While the law does not contain an express public enforcement provision, we would expect violations to be actionable by the Attorney General and other public prosecutors under California's Unfair Competition Law (UCL), which treats a violation of any law as an unlawful business practice. The California AG took that approach in its 2025 action against Illuminate Education, pleading KOPIPA violations as unlawful business practices under the UCL. Under the UCL, the AG and authorized prosecutors can seek injunctive relief and civil penalties of up to $2,500 per violation. 

What to do now 

Companies subject to KOPIPA should begin assessing the technical and operational changes needed to comply before January 1, 2027, including: 

Reassess scope. Review school-facing and mixed-use products to determine whether the company has actual knowledge of student use and whether each product is designed or marketed for school purposes. Consider sales and marketing materials and the information received through customer contracts, sales and onboarding processes, product configurations, and other school-specific interactions when conducting that assessment. 

Map AI uses. Determine where student data is used in AI training or development. Assess whether each use is restricted to serving only school purposes, including whether any model trained on student data is only deployed in connection with the school services. 

Update sensitive data inventories. Identify and restrict collection and/or use of reproductive/sexual health, immigration status, sexual orientation, or gender identity. And in the case of higher ed, precise geolocation information. 

Document retention and deidentification practices. Establish and operationalize a retention schedule tied to the purposes for which covered information is collected and document the company’s deidentification standards. Ensure both are suitable for sharing with schools and LEAs upon request, accurately reflect the company’s actual practices, and are consistently followed. 

Build school and LEA-level configurability. Develop the technical functionality needed to configure retention periods and deidentification standards at the school or LEA level, where required. 

Update rights-request workflows. Update processes for handling deletion and access requests to include education data of students subject to CCPA exceptions. The process should verify the requester’s identity and authority and, for deletion requests, require documentation that the student has been unenrolled for at least 60 days.


Susan Hintze is the Founder and Co-Managing Partner at Hintze Law PLLC. Recognized by Chambers, Legal 500, & Best Lawyers. Susan serves on the International Association of Privacy Professionals (IAPP) Board of Directors and is an IAPP Westin Emeritus Fellow. She is also co-chair of the firm’s Regulatory Defense Group and Kids + Teens Group. Susan has provided legal counsel to tech and e-commerce clients for over 25 years, of which, over 20 years have been focused exclusively in the area of privacy, AI, online safety, disinformation, and cybersecurity. 


Emily Litka Sanford, Of Counsel at Hintze Law PLLC, is co-chair of the Kids & Teens Group and a member of the Artificial Intelligence + Machine Learning Group and focuses her practice on global AI, privacy, and online safety laws and regulations. She regularly counsels on risk during product development, the development and operationalization of privacy programs, the preparation of data protection impact assessments, and the development of internal AI & privacy policies and processes.


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.


Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Introducing Data Across the Pond: American Data Law Through a Transatlantic Lens 

Hintze Law has launched its first podcast, Data Across the Pond with Hintze.  This new podcast will explore how the U.S. is regulating AI, privacy, and cybersecurity, and will discuss how this compares to UK and European approaches.   

Hosted by Sam Castic, a U.S. lawyer and head of the firm's London office, Data Across the Pond will feature conversations with UK and EU leaders for AI, privacy, and cybersecurity that cover the key developments and emerging issues global leaders should know in the States.  The conversations will provide practical insights for global and multinational organizations to address these issues and risks with scalable strategies and approaches. 

In our first episode, Sam Castic, Hintze Law Partner, is joined by Gemma Witham, Deputy General Counsel at Skyscanner, for a discussion on how the United States approach to AI regulation compares to the United Kingdom and European Union.  

The conversation explores how the EU has adopted a comprehensive regulatory framework through the EU AI Act, while the UK has taken a more sector-based approach that leverages existing laws and regulators. The discussion also highlights the evolving U.S. landscape, where a growing number of state laws are shaping how organizations approach AI governance in the U.S.  

Beyond regulation, the episode focuses on practical strategies organizations can adopt today to scale AI governance and risk management strategies to navigate this changing regulatory environment around the globe.  

The episode concludes with a forward-looking discussion about the future of AI governance, the challenges of regulatory fragmentation across jurisdictions, and the responsibility organizations have to promote the safe and ethical use of AI.  

Whether you are a legal or compliance professional, AI or privacy leader, or business executive navigating AI adoption, Data Across the Pond aims to provide practical insights and informed perspectives on the issues shaping the future of data law. 

We look forward to continuing these conversations in future episodes, and for now, check out our first episode on Spotify, YouTube, or Apple podcasts.


Sam Castic

Sam Castic is a Partner with Hintze Law, chair of the firm’s Retail Group, and co-chair of the Cybersecurity and Breach Response Group and FinTech + Financial Services Group. As a former chief privacy officer, he helps companies build, scale, and right-size privacy programs and strategies.


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

10 Ways to Avoid Privacy Risks Revealed in AI Notetaker Suits

By Jennifer Ruehr (August 28, 2026)

On Aug. 13, the U.S. District Court for the Northern District of California allowed significant portions of the proposed class action in In re: Otter.ai Privacy Litigation to proceed.

The suit, first filed in August 2025, challenges Otter.ai Inc.'s transcription and AI notetaking services. The plaintiffs allege that the company's meeting assistant joined virtual meetings, recorded and transcribed conversations in real time, collected voice-related information, retained meeting content, and used that information to improve its products and machine-learning systems.

Key Rulings From the Otter.ai Order

The ruling addressed several important privacy and communications-law issues, and reflects a common theme across claims involving standing, the Electronic Communications Privacy Act, the California Invasion of Privacy Act and the Illinois Biometric Information Privacy Act: When a vendor captures, retains or uses conversation content or voice-related data for its own business purposes, an AI transcription tool may look less like a passive service provider and more like an independent actor raising privacy, wiretap, and biometric risks.


Read the full article on Law360 or here.


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on data protection including AI, privacy, and data security. Hintze attorneys and data consultants support technology, advertising, media, fintech, health, biotech, ecommerce, and mobile industries.


Jennifer Ruehr is Co-Managing Partner at Hintze Law PLLC and co-chair of the firm’s Workplace Privacy Group, Cybersecurity and Breach Response Group, and the Artificial Intelligence and Machine Learning Group. Jennifer advises a diverse range of clients, including leading technology, automotive, airline, telecommunication, publishing, and media companies to innovative start-ups. She provides business-focused, actionable legal advice on privacy program development, AI risk management, and complex data agreements.

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Law Opens London Office  

Hintze Law is pleased to announce the opening of its London office--Hintze UK Ltd.  

Hintze UK Ltd. serves as a bridge between Hintze Law and its growing number of clients based in, or with offices in, the UK, Europe, and beyond. Our new location in London, one of the world's leading centers for business, technology, and finance, better enables Hintze to provide the practical and actionable advice on U.S. data governance laws that Hintze Law is renowned for, from within a European time zone more convenient for our international clients.  

The London office is led by Sam Castic, a US-law-licensed Partner at Hintze Law with nearly two decades of experience advising organizations on AI, privacy, and cybersecurity law. Before joining the firm, Sam served as Chief Privacy Officer at Blackhawk Network, a global fintech company with B2B and B2C products. Sam also led a team of privacy professionals as Head of Privacy at Nordstrom, a leading high-end U.S. fashion retailer. Sam leverages this experience to provide clients with actionable advice on US AI, privacy, and cybersecurity law. He also helps companies build, scale, and right-size data governance programs.  Sam chairs Hintze Law’s Retail Group, and co-chairs the Cybersecurity & Breach Response and FinTech & Financial Services Groups. He is a recognized U.S. privacy and data security lawyer by Chambers & Partners in both its USA and Global Guides, and is a Certified Artificial Intelligence Governance Professional (AIGP).  

The opening of the London office marks the latest chapter in the firm's continued growth under the co-management of Jennifer Ruehr and Susan Hintze. Founded in 2014 by Susan Hintze and later joined by Mike Hintze, Hintze Law was established to integrate regulatory insight, business strategy, and deep technical fluency to help global brands and high-growth innovators manage risk, seize opportunities, and navigate changing laws with confidence. Over the past decade, the firm has grown from a solo privacy practice into an internationally recognized law firm focused exclusively on the complexities of artificial intelligence, privacy, and cybersecurity. Today, its professionals, comprised of former in-house lawyers and expert technologists, are located throughout the U.S. and in the U.K., serving clients throughout the United States, United Kingdom, Europe, and around the world. 

The firm advises organizations ranging from emerging companies to Fortune 500 businesses across technology, financial services, healthcare, automotive, gaming, media, advertising, retail, and other highly regulated industries. Known for combining deep subject-matter knowledge with practical business advice, Hintze Law works closely with clients to address some of the most significant legal and policy developments affecting technology, data, and innovation today.  

Hintze Law and its attorneys have earned accolades from Chambers Global, Chambers USA, Legal 500, Best Lawyers, Super Lawyers, and Global Data Review's GDR 100, and others that recognize the world's leading data law firms. The firm is also a minority-owned, woman-owned, LGBTBE-owned, and NAMWOLF-certified law firm.  

As organizations continue to navigate increasingly complex legal and regulatory obligations across jurisdictions, Hintze UK Ltd. reflects the firm's longstanding commitment to serving clients whose operations, technologies, and compliance challenges span international borders.  


"Hintze UK Ltd is a private limited company incorporated in England and Wales (company number 17161767) with its registered office at 41 Lothbury, London, United Kingdom, EC2R 7HF" 


Key Contacts 

Sam Castic 

UK Managing Partner 

sam@hintzelaw.com 


Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Law Global AI Legal Updates 

Hintze Law’s Global AI Update provides a curated overview of key AI-related legal and regulatory updates. We spotlight new developments and emerging trends to help organizations that are developing, deploying, or relying on AI technologies to stay ahead of what’s next. 

Please also check out our latest Global Privacy Updates post. 

If you’d like to receive email alerts for our blog posts, visit our blog page to sign up. 


US AI Updates   

Colorado Publishes Draft ADMT and Chatbot Regulations 

On August 11, 2026, Colorado’s Attorney General announced it published draft regulations under the state’s ADMT Act (SB26-189, the replacement to the AI Act) and Chatbot Safety Act (HB26-1263).  The draft ADMT-focused regulations include detailed requirements for: 

  • consumer disclosures and accessibility standards; 

  • “midstream developers” that integrate covered ADMT into their own covered ADMT products;  

  • documentation and disclosure requirements for ADMT developers;  

  • when and how adverse outcome disclosures need to be provided to consumers, and what these must indicate about the decision and available consumer rights (including requirements that differ by sector and context—education, real estate, financial or lending services, insurance, and employment); 

  • how deployers need to respond to consumer requests for information about covered ADMTs; and 

  • how deployers need to authenticate consumers and honor consumer rights to (1) obtain personal data used in consequential decisions; (2) correct incorrect or inaccurate personal data used for consequential decisions; and (3) obtain human review and reconsideration of consequential decisions. 


The draft Chatbot Safety Act regulations have additional detail on exemptions and requirements for certain conversational AI services, including requirements for age assurance (and incorporation of an ISO standard for age assurance), consumer disclosures and accessibility, minor accounts and users, privacy and account settings, service design and operation, false representations, and annual report requirements. 

Comments are being accepted through October 26, 2026, and there will be a hearing on October 26, 2026. The regulations if adopted would take effect January 1, 2027. 

California AI Transparency Act Now in Effect  

On August 2, 2026, California's AI Transparency Act disclosure obligations became operative. The law applies to creators of publicly available generative AI systems with more than 1 million monthly visitors in California and requires covered providers to offer AI detection tools and implement both latent and manifest disclosures for AI-generated image, video, and audio content. Additional requirements take effect on January 1, 2027. 


Global AI Updates   

EC To Begin Enforcing AI Act Provisions 

The European Commission announced on July 30, 2026, that its AI Office, together with national authorities, would begin enforcing the European Union's Artificial Intelligence (AI) Act on August 2, 2026.  

NIST Publishes Initial Draft of Framework for Evaluating AI Systems 

On August 2, 2026, the National Institute of Standards and Technology (NIST) published an initial public draft of the TEVV-Athlon Framework (NIST AI 200-2) for public comment. The Test, Evaluation, Verification and Validation (TEVV) Framework is a structured approach for developing assessments of AI systems. The framework is meant to help AI system evaluators create an AI assessment (which the draft calls a "TEVV-Athlon." The framework consists of four stages: (1) articulate & organize, (2) define & construct, (3) apply & measure, and (4) synthesize & interrogate. The TEVV-Athlon assessment is meant to dovetail with the core functions of the NIST AI Risk Management Framework (RMF). The draft is open for public comment until October 6, 2026. 

Claude Introducing AI Content Marking 

Anthropic has signed the EU AI Act’s Article 50(2) Code of Practice on Transparency of AI-Generated Content and, per its Help Center article, is rolling out machine-readable content marking across Claude models and platforms. Anthropic is rolling out global, machine-readable content marking across all Claude models and platforms. The system weaves imperceptible, copy-persistent watermarks into generated text and attaches cryptographic C2PA metadata to visual files. This means any material generated or processed through Claude — whether via web, API, or enterprise cloud partners — will automatically carry compliance signals without altering text quality or user experience. Anthropic plans to release dedicated detection mechanisms and technical guidance, allowing developers and organizations to programmatically verify whether a piece of text or a file carries a supported Claude mark. 

For more information about this process refer to: How Claude marks AI-generated content | Claude Help Center 


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.  
Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Lawyers Recognized in the 2027 Editions of Best Lawyers

Hintze is pleased to announce that eight of its lawyers have been recognized in the 2027 editions of The Best Lawyers in America® and Best Lawyers: Ones to Watch® in America. This recognition spans the firm's core practice areas of artificial intelligence, privacy and data security, technology, information technology, and advertising law, reflecting the breadth of experience the firm brings to clients navigating complex legal and regulatory challenges.  

Among this year’s honors, Mike Hintze, a Member Partner at Hintze Law PLLC and chair of the firm’s Health and Biotech Privacy Group, was named the 2027 "Lawyer of the Year" in Seattle for both Information Technology Law and Technology Law. The distinction is awarded to a single lawyer in each practice area and geographic market who receives the highest overall peer feedback. Mike was also recognized in the 2027 edition of The Best Lawyers in America® for Artificial Intelligence Law, Information Technology Law, Privacy and Data Security Law, and Technology Law. A former Chief Privacy Counsel at Microsoft, Mike advises leading global companies on privacy, cybersecurity, artificial intelligence, and technology law matters and has been recognized by Best Lawyers since 2024. 

The 2027 edition of The Best Lawyers in America® recognizes Sam Castic, Susan L. Hintze, and Taylor Widawski. Sam, a Partner at Hintze Law, chair of the firm’s Retail Group, and co-chair of the Cybersecurity and Breach Response Group and FinTech + Financial Services Group, was recognized in Artificial Intelligence Law, Information Technology Law, Privacy and Data Security Law, and Technology Law. Drawing on experience from leadership roles at Blackhawk Network and Nordstrom, he advises clients on emerging technology, AI governance, privacy, and digital innovation. Susan, the Founder and Co-Managing Partner and co-chair of the firm’s Regulatory Defense Group and Kids + Teens Group, was recognized in Advertising Law, Information Technology Law, Privacy and Data Security Law, and Technology Law. She has spent more than 25 years advising organizations on complex privacy, data security, advertising, and technology matters and has been recognized as “Lawyer of the Year” by Best Lawyers® for Information Technology Law in Seattle for 2026. Taylor, a Partner at Hintze Law PLLC and co-chair of the firm’s Artificial Intelligence and Machine Learning Group and FinTech + Financial Services Privacy Group, was recognized in Privacy and Data Security Law and Technology Law and counsels clients on AI, privacy compliance, data governance, and technology-related legal issues. Before joining Hintze Law, Taylor was in-house privacy counsel at T-Mobile and Chime Financial and has been recognized by Best Lawyers since 2026, when she was included in Best Lawyers: Ones to Watch® in America for Technology Law. 

The firm's emerging leaders were also recognized in the 2027 edition of Best Lawyers: Ones to Watch® in America. Emily Litka Sanford, Of Counsel at Hintze Law and co-chair of the Kids & Teens Group and a member of the Artifical Intelligence + Machine Learning Group, is recognized in Privacy and Data Security Law, advises organizations on privacy compliance, product counseling, and evolving regulatory requirements. Cameron Cantrell, also recognized in Privacy and Data Security Law, focuses her practice on privacy, cybersecurity, and regulatory counseling and has been recognized by Best Lawyers since 2026.  Felicity Slater, likewise recognized in Privacy and Data Security Law, counsels clients on privacy and technology issues arising from the collection, use, and governance of personal data and has been recognized by Best Lawyers since 2026. Hansenard Piou was recognized for Privacy and Data Security Law and advises clients on privacy, data protection, and compliance matters across a range of industries. He has also been recognized by Best Lawyers since 2026. 

Founded in 1981, Best Lawyers is among the legal profession's longest-standing and most respected peer-review publications. For more than four decades, its methodology has relied on confidential evaluations from lawyers assessing the professional abilities of their peers within the same practice areas and geographic markets. Recognition is based on a structured process that includes nomination, peer review, analysis of feedback, and verification of professional standing, and lawyers cannot pay to receive recognition. As a result, inclusion in Best Lawyers is widely regarded as a meaningful acknowledgment of professional excellence and the confidence of one's peers. 

The firm congratulates Mike Hintze, Sam Castic, Susan L. Hintze, Taylor Widawski, Emily Litka Sanford, Cameron Cantrell, Felicity Slater, and Hansenard Piou on their inclusion in the 2027 editions of Best Lawyers. And we thank all of our peers for their generous support and time in recognizing our attorneys. 

______________________________________________________________ 

Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.  
Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

How Data Broker Laws are Reaching Consumer-Facing Companies

New Jersey enacted a sweeping new data broker law on June 30, days after it was proposed. While its potential for seven-figure registration fees and expansive scope have gotten a lot of attention, there's another trend that the New Jersey law advances: State data broker laws are now applying to companies that have never been thought to be data brokers — i.e., consumer-facing companies that deal with customer and first-party data.


Law360 recently published an article that Sam Castic wrote about this.  Click here to view the article.


Sam Castic is a Partner with Hintze Law, chair of the firm’s Retail Group, and co-chair of the Cybersecurity and Breach Response Group and FinTech + Financial Services Group. As a former chief privacy officer, he helps companies build, scale, and right-size privacy programs and strategies.

Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.


Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Law Global Privacy Updates 

The Hintze Law team continues to monitor global privacy and data security developments to provide timely, practical insights for clients. Below is a summary of key updates from early June to late July 2026. For developments in AI, please see our latest Global AI Updates. 


US Privacy Updates   

California Privacy Protection Agency Announces First Audit Focused on Worker Privacy Rights  

The CPPA announced that the newly established Audits Division has begun its first formal privacy audit focused on gig economy platforms (app-based transportation, delivery, task services, etc.) operating in California. The audit will focus on compliance with data subject rights for employees, independent contractors, and consumers. The announcement focuses on the right to access personal information and to know about data practices, and indicates it will examine whether access requests are being processed compliantly, timely, and completely.    

This audit shows a growing CPPA focus on state privacy rights and obligations owed to employees and independent contractors. The announcement also indicates that this is “the first in a series of sectoral audits” so other companies and sectors are likely to be targeted in the future.  


Connecticut Attorney General Announces CTDPA Guidance  

On July 2, 2026, the Connecticut AG posted guidance directed towards “big tech” announcing that new amendments to the CTDPA entered into effect on July 1, including:  

  • Rights and safeguards for kids online; 

  • Expansion of scope;  

  • Expansion of “sensitive data”; 

  • New consumer rights; and 

  • New rights with respect to profiling decisions made through automated means.  


Delaware Amends the Delaware Personal Data Privacy Act  

Delaware amended the Delaware Personal Data Privacy Act (DPDPA).  The changes take effect January 1, 2027, and include:  

  • Broader applicability: Lower personal data thresholds for applicability;  

  • Applicability to third parties: Specific obligations on “third parties” that acquire personal data from a controller;  

  • New data subject rights: Creates rights (1) to know how data is used for certain profiling, and (2) to obtain a list of the specific third parties that receive personal data;  

  • Third party obligations: Specific due diligence and contract provision requirements when disclosing personal data to third parties (including those used for targeted advertising);    

  • Obligations for “reports”: Controllers that provide “reports” (including personal data, summaries, or results of automated decisions) to third parties have specific contractual and data subject rights obligations that may impact how services can be provided (these requirements may also apply to reports in the employment context);  

  • Sensitive data: Expands the definition of sensitive data to include inferences, neural data, financial account numbers and credentials, and government identification numbers.  It also requires necessity and proportionality to a disclosed purpose (along with consent) before sensitive data can be processed, and restricts when sensitive data can be sold;  

  • Profiling assessments: Details specific matters that need to be included in a data protection assessment when personal data is processed for certain profiling decisions; and   

  • Narrower GLBA exemption: Narrows the GLBA entity-level exemption (excluding many fintechs and other financial institutions) but retains the data-level GLBA exemption  


Hawaii Passes Social Media Data Deletion Act  

Hawaii passed the Social Media Data Deletion Act.  The law requires covered social media platforms to give users an accessible way to delete their accounts, permanently erase all associated personal and sensitive personal information within 90 days, and refrain from deceptive “dark pattern” tactics that interfere with deletion rights.  The law is enforced by the Attorney General and took effect July 1, 2027.  


Illinois Enacts Digital Age Assurance Law    

Illinois enacted the Children’s Online Social Media Safety Act (HB5511).  It has obligations for:  

  • Covered manufacturers: Certain Internet-connected device manufacturers, operating system providers, and app stores that allow users to set up accounts must collect and share user age information;  

  • Covered Platforms: Websites, online services, and apps that have certain social interaction components must request age information from covered manufacturers, and have a number of service design and functional requirements for accounts used by minors.  

The law will take effect January 1, 2028, and is enforceable by the Attorney General.  


Kentucky Comprehensive Privacy Act Risk Assessment Requirement is now in Effect  

The KCDPA Data Protection Impact Assessment obligations became effective on June 1, 2026.    


Minnesota Strengthens Social Media Law and Adds Private Right of Action  

Minnesota has passed HF 4138, which amends existing law to further regulate social media platforms.  Covered social media platforms include websites or apps that are open to the public, allow user account creation, enable communication with other users for the purpose of posting content, and has certain features or targeted advertising.   

Requirements include detailed age estimation requirements, requires collection of months and years of birth at account creation, parental consent and parental setting requirements for a child accounts, high default privacy settings for child accounts, and restrictions on addictive interface features and targeted advertising for child accounts.  There are specific requirements for terminating child accounts on request of the account holder, parent, or when age estimation suggests an account is a child’s account and verifiable parental consent hasn’t been obtained.    

The law includes a private right of action, and plaintiffs can recover general and special damages, attorney fees, and other costs for negligent, reckless, or knowing violations of the law.  For reckless or knowing violations, plaintiffs can also collect the greater of actual damages or $10,000 in statutory damages (and punitive damages if a consistent pattern of such conduct is found). The law takes effect July 1, 2027.  


New Hampshire Amends Privacy Law to Ban Sale of Children’s Data  

On June 19, 2026, HB1460 was signed into law. The bill amends New Hampshire’s Data Protection Act to prohibit selling a child’s personal data. The law is effective as of January 1, 2027.  


New Jersey Passes Age-Appropriate Design Code  

On June 30, 2026, the New Jersey legislature passed the New Jersey Kids Code Act. The law is similar to other age-appropriate design codes, requiring data minimization, prohibiting facilitation of targeted advertising, and privacy defaults for minors. The law’s requirements include setting privacy defaults for a covered minor to the highest level of privacy, providing an account deletion/un-publication tool, designating an officer as responsible for the covered online service provider’s compliance, and posting annual public reports prepared by independent third-party auditors no later than January 1st of each year. The law also specifies that “covered online service provider” excludes providers of online services where more than 98% of users are known to be adults.  


New Jersey Amends Privacy Law and Regulates First-Party Data Collectors as Data Brokers  

New Jersey quickly proposed and enacted a bill that amends the state's comprehensive privacy law to prohibit sales of sensitive data.       

The bill also has a unique set of new requirements for "data brokers" and "data collectors" that will apply to a number of different businesses, not just those who have data broker business models. Data collectors include businesses and business units that sell or license personal data of consumers they have direct relationships with to data brokers.   Data collectors and data brokers both have to register with the state next year, with registration fees of up to $1,500,000. The Division of Consumer Affairs indicated that data broker registration will be open from April 1, 2027 - June 30, 2027, and regulations are also expected. News reports have indicated that amendments may also be considered for the law.  

The approach to regulating "data collectors" could sweep in companies that use tracking technologies on their websites or mobile apps (if any are provided by data brokers under the law; many are). It could also apply to companies that share data with vendors--such as advertising, adtech, fraud, and risk vendors--when those vendors are classified as data brokers under the law. This may be true even if those vendors are subject to data processing agreements, or otherwise agree to act as data processors or service providers.  

We have a blog post here that explores how recent state law changes expand the companies that data broker laws regulate.  


New York Enacts Safe by Design Act  

New York enacted a law (as part of a broader budget bill) that regulates certain websites, online services, and apps (“covered platforms”) that: (1) are used by minors; (2) allows users to create public or semi-public profiles; (3) offers mechanisms for private communications with other users and either (i) the ability to create or post media for other users to see and respond to or the ability to create games or immersive digital environments for other users to play along with in-game purchases. Covered platforms have requirements for: age assurance for users; specific default settings and service limits for minors; parental controls, features, and notification obligations; and restrictions on certain integration AI companion features. The law will be enforced by the attorney general with statutory damages of up to $5,000/violation, and the Attorney General is required to have a website to intake complaints, information, and referrals from the public regarding alleged noncompliance with the law. Regulations are authorized, and the law takes effect January 1, 2027.  


Ohio Social Media Law Unblocked  

On June 18, 2026, the Sixth Circuit vacated a lower court’s ruling that had blocked Ohio’s social media law from going into effect. Ohio’s Parental Notification by Social Media Operators Act (Ohio Rev. Code § 1349.09, originally passed in 2023) requires operators of social media websites, services, or products that have social features and that target children or are reasonably anticipated to be accessed by children to obtain verifiable parental consent. The Sixth Circuit found that NetChoice did not have standing to challenge on behalf of minors. The court also held that the law survives First Amendment strict scrutiny, finding that Ohio has a compelling interest in protecting minors from social media harms and that a parental consent requirement is sufficiently tailored to advance that interest.  


Vermont Expands Companies It Regulates as Data Brokers  

Vermont amended its data broker law to expand requirements for data brokers, and the types of companies that are considered data brokers.  Under the amendments data brokers now include:  

  • businesses or business units that sell or license any information, including derived data and identifiers, that is linked or reasonably linkable to a person or device;   

  • such businesses even if they collected the data directly from a consumer, if the consumer was not intending to interact with the business (e.g., potentially in the pixel, cookie, or tracking technology context); and  

  • such businesses that have a customer or other relationship with the consumer where they sell or license data they did not collect in a first-party interaction with the consumer.  

The law will: increase fees and required details for data broker registrations; require data brokers to disclose if they sell or share data with foreign actors, government entities, law enforcement, or generative AI model developers; require bonds; result in disclosure of data broker registration details on a government website.    

The law also has a unique set of data security breach notification requirements for data brokers that apply broadly to any breach of personal data (including many types that don’t trigger notification requirements in any other state), and that require individual and attorney general notifications.  The amendments take effect January 1, 2027.  


Vermont Enacts Comprehensive Privacy Law 

Vermont’s governor signed the Data Privacy and Online Surveillance Act, a comprehensive privacy law, into law.  The law has many parallels to Connecticut’s comprehensive privacy law, including provisions specific to consumer health data.  Some unique aspects of the law include:  

  • For data to be considered “deidentified” (and not personal data), it must also meet the HIPAA deidentification rule;  

  • A narrow definition of “publicly available information” which excludes consumer profiles on websites or data combined with publicly available information;  

  • Requiring privacy notices to disclose whether personal data is processed or sold to train large language models; and  

  • Specific content requirements for data protection assessments that involve profiling for certain legal or similarly significant effects.  

The law takes effect January 1, 2028.    


SCOTUS Upholds FCC’s Ability to Issue Forfeiture Penalties   

The United States Supreme Court held that FCC forfeiture orders do not violate the seventh amendment right to a jury trial. The case was FCC v. AT&T, Inc. and related to forfeiture orders issued in connection with location data privacy matters.   


SCOTUS Decision on Geofence Warrants and the Fourth Amendment  

The United States Supreme Court held that an individual has a reasonable expectation of privacy in their cell-phone location information. Location data gained from geofence warrants is considered a Fourth Amendment search. The case was Chatrie v. United States. Previously, in Carpenter v. United States, the Court held that cell-site location information (CSLI) constituted a Fourth Amendment search and that allowing government access to cell-site records contravenes expectations of privacy. Everything Carpenter relied on to find that law enforcement conducted a Fourth Amendment search when they accessed CSLI applies as well or better to police accessing Google Location History data. The Court rejected both the argument that accessing only a short amount of cell-phone location data does not count as a Fourth Amendment search and the third-party doctrine. This decision could have wide implications for government access to cell-phone location data, as the Court specified that a cell-phone user is not to be viewed as sharing private information with third parties – which then can be freely passed on to the government – just by doing the ordinary things cell-phone users do.  


Court Wiretap Ruling Based on Alleged DOJ Rule Violation May Increase Wiretap Claims and DOJ Rule Compliance Risks     

A court has allowed Wiretap Act (ECPA) claims to proceed against a company that shared website visitor data with a Chinese advertiser in alleged violation of the DOJ Rule on Access to U.S.  Sensitive Personal Data by Countries of Concern.   

A federal district court in Illinois denied a motion to dismiss in Baker v. Index Exchange, Inc., allowing a novel Electronic Communications Privacy Act (ECPA) claim to proceed against Index Exchange, a Canadian adtech company. The plaintiff alleged that Index Exchange, which acted as a supply-side platform for BibleGateway.com, collected website visitor information through tracking technologies and shared ad bidding and related data with Temu, a company alleged to be a "covered person" under the Department of Justice's Bulk Sensitive Personal Data Rule. Ordinarily, such claims would be difficult to pursue under the ECPA because the statute generally permits interceptions where one party has consented. However, the court found that the plaintiff had plausibly alleged the ECPA's crime-tort exception applied because the data transfers may have violated the DOJ Rule, which carries both civil and criminal penalties.  

The decision is significant because it opens a potential new pathway for privacy plaintiffs to challenge the use of tracking technologies and cross-border adtech data flows. Although Index Exchange argued that it was not subject to the DOJ Rule because it is a Canadian company, the court found the plaintiff's allegations sufficient at the pleading stage, noting that the Rule can also apply to certain U.S. persons acting on behalf of foreign entities. The ruling may encourage additional ECPA litigation involving companies that share advertising, bidding, or analytics data with organizations connected to China or other countries of concern, particularly where plaintiffs allege underlying violations of the DOJ Rule.


HHS Settlement with Employer Group Health Plan Underscores HIPAA Obligations for Employers 

The HHS OCR entered into a resolution agreement with the employer-sponsored group health plan of Spencer Gifts LLC, over alleged violations of the HIPAA Privacy and Security Rules relating to a ransomware attack.  The agreement included a $450,000 penalty.  Spencer Gifts allegedly failed to conduct a HIPAA security risk assessment before the breach, and did not have required policies and procedures to address HIPAA breach notification requirements.    

HIPAA compliance isn’t always a focus area for organizations that sponsor health plans for their employees, and this case is a reminder that there are enforcement risks.   


Global Updates 

Brazil's ANPD Begins Monitoring App Store Compliance with ECA Digital Law 

Brazi's ANPD announced on June 10th that it has started monitoring app store and operating system providers for compliance with the age verification and age signal requirements in the ECA Digital Law. The announcement specifically calls out that the monitoring is focused on Apple, Google, and Microsoft. The notified companies must submit, within 15 days, information and documents relating to system architectures, data flows, age verification mechanisms, internal policies, and other documents demonstrating compliance.  

The ANPD also launched a specific page for submitting complaints regarding ECA Digital violations: Denúncias - Eca Digital.  


Brazil's ANPD Concludes Initial DPO and DSAR Compliance Monitoring 

On July 3, 2026, the ANPD announced that it had concluded the first phase of two monitoring processes related to compliance with DPO requirements and related to the availability of communication channels between controllers and data subjects. Of the 56 organizations monitored, 27 fully complied with the ANPD, 8 still have pending issues that must be corrected, and 21 did not respond to the ANPD's request for proof of compliance. The ANPD is considering sanctions for the nonresponsive organizations. The news release lists out which organization fell into which category. The ANPD also gave some context for why they chose their monitoring targets as they did - some were selected for monitoring based on an audit by another federal agency, and others were selected based on the analysis of complaints from data subjects that pointed to a lack of a DPO or deficiencies in the contact channels available to data subjects.  


Mexican State of Jalisco Bans Social Media for Minors Under 14  

The Mexican State of Jalisco published a new law on June 2 to guarantee the rights of girls, boys, and adolescents in digital environments. The law bans the use of social media for any minors under the age of 14, and requires the implementation of digital supervision and protection mechanisms in educational and municipal settings. The law also creates a State Council for the Protection of Girls, Boys, and Adolescents in Digital Environments, composed of state agency and private educational institution representatives, which must be convened within 30 days. Municipalities have 120 days to harmonize their regulations and adapt their provisions to the requirements in the law. Penalties for non-compliance include warnings, fines, temporary suspension of activities, or revocation of municipal permits and licenses, as appropriate.  


EDPB Publishes Draft Common Data Breach DPA Notification Template  

On June 10, 2026, the EDPB announced a common data breach notification template for compliance with the GDPR Article 33 requirement to notify Data Protection Authorities (DPAs). It is designed to be implemented by DPAs via an IT tool.  

The template was open to public consultation through August 5, 2026, after which the EDPB will decide on the timeline for DPAs to implement the template. 


European Parliament Publishes Assessment of Cybersecurity Act 

On June 12, 2026, the European Parliament announced its impact assessment of the Cybersecurity Act, supporting "the revision of the ECCF to expand and clarify its scope and improve its governance and procedures; targeted amendments to the NIS2 Directive to facilitate and align compliance across the internal market; the filling of regulatory gaps by setting up an EU-level framework to enhance ICT supply chain security against non-technical risks." 

The assessment highlights four current problems for remediation: 

  • Misalignment between the Union's cybersecurity policy framework and stakeholders' needs in an increasingly hostile threat landscape. 

  • Stalled implementation of the ECCF. 

  • Complexity and diversity of the cybersecurity-related policies impacting the Union's cyber posture. 

  • Increasing ICT supply chain security risks. 


The French Parliament Approves Social Media Ban for Minors Under 15  

France has become the first EU member state to approve a social media ban for minors when the French parliament approved legislation blocking minors under 15 from accessing social media platforms. The ban also includes provisions to ban the use of mobile phones in high schools.  

Emmanuel Macron has indicated that he wants the law to take effect in September to align with the start of the new school year. However, the bill must first go through constitutional review before it can take place.  


German Federal Office for Information Security Announces IT Security Guidelines For Medical Practices 

On July 14, 2026, the Federal Office for Information Security (BSI) announced guidelines for medical practices for implementing cybersecurity requirements under the new IT Security Guidelines pursuant to Section 390 of the Social Code Book V (SGB V).  

The requirements depend on the size of the medical practice: 

  • A small practice has up to five people constantly in charge of data processing. 

  • A medium practice has 6 to 20 people constantly in charge of data processing. 

  • A large practice or a practice with extensive data processing has more than 20 people constantly in charge of data processing, or a medical practice that handles data processing beyond the normal data transmission (e.g., large medical centers with hospital-like structures, large labs). 

Each practice must complete requirements from particular Annexes, as detailed in the guidelines, whose requirements include regular software updates and data backups, implementing access protection and email security measures, evaluating the security of cloud services, and providing structured training for new employees to recognize attack patterns. 

The press release and quick-check brochure are also available in German. 


Latvian Cabinet of Ministers Amends Timelines under Medical Document Management Regulations 

On June 9, 2026, the Latvian Cabinet of Ministers issued Regulation No. 322, amending Regulation No. 265 on the Procedures for the Management of Medical Documents for healthcare institutions and professionals: 

  • Where medical treatment institution has been entered into the information system in full, it must be retained for three months after providing the healthcare service, 

  • Where medical treatment institution has been partially entered into the information system, it must be retained under Article 35's previous retention periods. 


ICO Publishes Final Guidance on Consumer IoT products  

On June 11, the UK ICO published its finalized guidance for consumer IoT products and services. The guidance includes regulatory certainty around how to ask for informed consent, how to provide transparent privacy information, and what tools need to be available for consumers to exercise their data subject rights.   

Of note that the announcement also says that the ICO is turning their attention to connected TVs, "engaging with connected TV manufacturers this year to assess whether they are complying with the law and offering consumers meaningful choice over how their data is used."   


UK Announces Social Media Ban For Under-16s 

The UK announced a social media ban for under-16s, following a national consultation from March to May 2026. The first set of Regulations is expected before the end of this year, with the changes to be implemented in spring 2027. Former Prime Minister Keir Starmer stated the ban will be "going further" than others, including not just social media sites and apps, but will also include restrictions on communications with children on gaming and livestreaming platforms with chat features. 


UAE Issues Legislation Banning Social Media for Children Under 15  

On June 17, 2026, the UAE issued Cabinet Resolution No. 106 of 2026 Regarding the Regulation of Children's Access to Social Media Platforms. The effective date was June 30, 2026. There is a 12-month transition period from the effective date for compliance. The resolution prohibits children under 15 from creating, using, or operating any personal account on Social Media Platforms subject to the provisions of the resolution. For children between 15 and 16, access is permitted but with special restrictions. The resolution sets out obligations for Social Media Platforms, Child Caregivers, and provides for oversight and supervision of Social Media Platforms by UAE regulatory authorities.  

Under the resolution, Social Media Platforms are required to: (1) implement approved and effective age verification mechanisms, (2) detect and delete accounts of children under 15, (3) adopt reasonable and appropriate technical and organizational measures to prevent circumvention of these restrictions, (4) refrain from targeting ads to children, (5) design and integrate digital awareness tools and materials within platforms interfaces directed at children and parents, (6) conduct periodic assessments of digital safety risks relating to children, (7) provide periodic reports to relevant authorities, and (8) any other obligations under law and implementing resolutions.  


Australia Privacy Commissioner Finds Privacy Breaches in Third-Party Tracking Pixel Investigation 

Australia's Privacy Commissioner found in two separate determinations that online health service providers Medmate Australia Pty Ltd (Medmate) and Monash IVF Pty Ltd (Monash) violated the APPs by collecting sensitive information without consumer consent, failing to take reasonable steps to notify individuals about the collection of their information, and using or disclosing that sensitive information for the purpose of direct marketing without individual consent (APPs 3.3, 5.1, and 7.1 respectively). 

Both determinations center around Medmate's and Monash's use of third-party tracking pixels. Particularly, the use of pixels which captured and transmitted full website URL strings back to social media and advertising platforms. Because user search queries or specific page pathways were embedded into the URLs, they inherently revealed sensitive health information. For example, a search for an oral contraceptive on Medmate would generate: medmate.com.au/online-prescriptions/telehealth-form/contraception, while a website visitor to Monash looking into "donor programs" would have that specific intent disclosed in the URL string. Medmate and Monash then used or disclosed this data to facilitate ad campaigns and targeted advertising on social media platforms. 

Regarding notice to the consumers, each determination highlighted different issues. Prior to the implementation of a cookie banner, Medmate relied entirely on changing privacy policies, which the OAIC stated contained inaccuracies and were insufficient as they were static notices. While Medmate eventually implemented a cookie consent banner, the OAIC found it to be insufficient because it was too vague. When the pop-up was introduced, it only referred generically to "cookies" rather than tracking pixels, failed to name the actual third parties receiving the data (Meta and TikTok), and was generally not specific enough given the highly sensitive nature of the health information. 

On the other hand, Monash did not provide a website cookie banner or pop-up notice at all. Instead, Monash relied entirely on its privacy policies that only mentioned "cookies" and "Google Analytics" which the OAIC deemed insufficient. 

This investigation followed a preliminary scan by the OAIC of 50 health service provider websites, alongside the publication of its formal guidance on the application of the Privacy Act to tracking pixels. 

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Law Global AI Legal Updates 

Hintze Law’s Global AI Update provides a curated overview of key AI-related legal and regulatory updates. We spotlight new developments and emerging trends to help organizations that are developing, deploying, or relying on AI technologies to stay ahead of what’s next. 

Please also check out our latest Global Privacy Updates post. 

To receive email alerts for our blog posts, sign up here. 


U.S. Updates 

Hawaii Passes the Artificial Intelligence Disclosure and Safety Act 

On July 14, 2026, Hawaii passed the Artificial Intelligence Disclosure and Safety Act. The law requires operators of AI companion services to clearly disclose to users that they are interacting with AI rather than a human, with more frequent and persistent disclosures required when the operator knows or has reasonable certainty a user is a minor. Operators must also adopt protocols to respond to user expressions of suicidal ideation or self-harm by directing users to crisis services, such as suicide hotlines and crisis text lines, and must prohibit their systems from representing themselves as licensed mental health professionals. 

Beginning January 1, 2028, operators must submit annual reports to the Behavioral Health Administration of the Department of Health detailing crisis referral counts and safety protocols. Violations are treated as unfair or deceptive acts or practices enforceable by the Attorney General, with civil penalties of up to $1,000 per violation capped at $1,000,000 per operator, but the law expressly forecloses a private right of action, distinguishing Hawaii from Oregon and Washington, which both grant individuals the right to sue directly. 

The law is effective immediately.   

New Jersey Passes the Fair Price Protection Act 

On July 23, 2026, New Jersey passed the Fair Price Protection Act. The law prohibits the use of for "surveillance pricing or any other pricing strategy that determines or varies the sale price of groceries and other foodstuffs based, in whole or in part, on personal data," with exceptions for reasonable costs associated with providing such goods to different consumers, bona fide discounts for disclosed conditions or criteria, or bona fide discounts offered as a part of loyalty program. 

The law also establishes a one-year moratorium on the new use of "electronic shelf labels," meaning a "electronic display that presents the product and pricing information for groceries and other foodstuffs including, but not limited to, labels that are visible to the consumer only after the consumer has scanned a quick-response (QR) code, barcode, or other code."  

The Attorney General may bring a civil action for the violation of this act and any regulations adopted pursuant to it. 

The moratorium takes effect on February 1st, 2027, and the remaining provisions take effect on August 1st, 2027. 

Illinois Enacts AI Safety Measures Act 

On July 6, 2026, the Illinois passed the Artificial Intelligence Safety Measures Act.  The law applies to certain frontier AI model developers and includes requirements for: establishing and publishing an AI framework that addresses specific matters; transparency; obtaining third party compliance audits; reporting certain safety incidents, and filing an annual disclosure statement with the state before deploying or operating a frontier model in Illinois.  

Most provisions will take effect January 1, 2027 (framework and audit requirements become effective January 1, 2028).  The law is enforced by the Attorney General with penalties not to exceed $1M for first violations or $3M for subsequent violations.   

Rhode Island Passes a Companion Chatbot Law 

On June 22, 2026, Rhode Island joined the states that have enacted a companion chatbot law. Its requirements include establishing protocols for addressing ideation of suicide and harm to others; filing annual reports with the office of the attorney general which include safety protocol metrics; and notifying the user at the beginning of and at least every three hours during AI companion that the user is not communicating with a human. 

The law takes effect January 1, 2027. 

CSA Publishes Draft Post-Mortem Report on OpenAI – Hugging Face Incident 

On July 27, 2026, the Cloud Security Alliance (CSA) published a draft post-mortem report of the OpenAI – Hugging Face Incident. The response follows an incident where OpenAI tested one of its agentic AI models (a model not deployed into production) in a closed environment without access to the open internet. Nonetheless, the model was able to break into Hugging Face production systems. The report highlights the incident as the first documented case of a fully autonomous attack and outlines some of the tell-tale signs of this kind of attack. Additionally, the report offers several key takeaways: proactively test and operationalize cyber-capable models, liberally deploy deception technology, and govern under the assumption that rogue agent behavior is the norm, not the exception.  

FTC Publishes Proposed Policy Statement "Concerning the Suppression of Accuracy in Artificial Intelligence Systems" 

On July 1, 2026, the U.S. Federal Trade Commission published a proposed policy statement "Concerning the Suppression of Accuracy in Artificial Intelligence Systems." The document suggests that the FTC is considering its powers under Section 5 of the FTC Act to investigate whether AI companies are altering their AI systems output to comply with state laws (like the Colorado AI Act) in a deceptive or unfair manner. 

Washington State AI Task Force Releases Final Report 

On July 1, 2026, the Washington Attorney General's Office released the final report of the state's AI Task Force: the capstone of a two-year effort by the 19-member body created under SB 5838. 

Across its three reports, the task force advanced 11 policy recommendations; during the 2025–2026 biennium the Legislature took up 8 and has already enacted 4 in whole or in part (including companion AI chatbots, transparency in healthcare prior-authorization decisions, disclosure of AI use by law enforcement, and enforcement against AI-generated CSAM). Furthermore, the final report outlines three policy recommendations pending legislative action: establishing an Emerging Technology Advisory Body, investing in K-12 STEM and higher education, and adopting the NIST Ethical AI Principles.  

Global Updates 

European Commission Publishes Implementing Regulation on GPAI Model Enforcement 

On July 20, 2026, the European Commission published Implementing Regulation 2026/1755 as part of the harmonized rules on artificial intelligence in relation to the EU AI Act. The Regulation concerns the evaluation of general purpose artificial intelligence (GPAI) models (per EU AI Act Article 92) and the fines for providers (EU AI Act Article 101). The Regulation takes effect August 10, 2026. It details the arrangements and conditions for GPAI evaluations, including the involvement of independent experts to conduct evaluations, how the experts will be selected, opening and closing of evaluation proceedings, procedural safeguards, and the protection of confidential information that may be obtained during evaluations. For the enforcement of penalties, the Regulation details limitation periods both for the imposition of penalties (5 years from the date of the prohibited conduct) and the enforcement of penalties (5 years from the decision adopting the penalty). Both limitation periods may be interrupted by a variety of actions on the part of the Commission.   

European Commission Publishes Guidelines on Transparency Obligations for Providers and Deployers of Certain AI Systems  

On July 20, 2026, the European Commission published guidelines defining the scope of transparency obligations under Article 50 of the EU AI Act. Among its subsections, the document provides guidance on: 

  • Requirements for providers of AI systems which are intended to interact directly with natural persons, such as voice assistants and chatbots, to design and develop such systems “in such a way that they disclose both their artificial nature and the person on whose behalf they are acting.” 

  • Requirements for providers of AI systems generating synthetic content to be marked so that natural persons can detect it as AI-generated or manipulated and verify its origin. 

  • Requirements for deployers of emotion recognition systems and biometric categorization systems to inform natural persons of their exposure to such systems by the first interaction with them. 

  • Requirements for deployers of generative AI systems to “clearly and distinguishably” disclose deep fakes and AI-generated or manipulated text “published with the purpose of informing the public on matters of public interest.” 

European Commission Publishes Action Plan on Cybersecurity and Artificial Intelligence 

On July 7, 2026, the European Commission published the Action Plan on Cybersecurity and Artificial Intelligence, focusing on complementary objectives: 

  1. Promoting the safe and responsible use of advanced AI 

  2. Reinforcing the EU's cybersecurity and resilience 

  3. Scaling up Europe's AI capabilities for cybersecurity 

The plan promotes and reinforces existing legal frameworks, including the NIS2 Directive, the Cyber Resilience Act, the NIS2 Directive, the Digital Operational Resilience Act (DORA) and the Cyber Solidarity Act.  

Slovenian Information Commission Publishes FAQs on Deepfakes 

On July 16, 2026, the Slovenian Information Commissioner published FAQs about privacy and data protection risks and obligations regarding deepfakes and generative AI content under the GDPR and EU AI Act. 

German DPA Publishes AI Assessment Framework 

On July 6, 2026, Germany's Federal Office for Information Security (BSI) announced a community draft of its Artificial Intelligence (AI) Audit and Assurance Assessment Architecture (A5). This assessment is meant for AI providers, operators, and developers to comply with assessment obligations under the EU AI Act, the Cyber Resilience Act and future standards, including those expected for the public sector. 

Feedback can be submitted to aisecurity@bsi.bund.de by filling the official form until August 31, 2026. 

Netherlands DPA Issues Generative AI GDPR Compliance Guide 

On July 13, 2026, the Dutch data protection authority, Autoriteit Persoonsgegevens (AP), has published its first substantive GDPR interpretation for generative AI: a guidance document (handreiking) for organizations developing generative AI models or putting them into use, and a step-by-step checklist (hulpmiddel) for those deciding whether to deploy. There is currently no English version of either the guidance or the checklist. 

The guidance addresses which legal bases can support model training, how to handle indirectly collected data, and what data cleaning, enrichment, and retention require.  The checklist also covers compliance requirements such as data minimization, DPIAs, Automated decision-making, and periodic reassessments. 

Since 2023, the AP has served as the national coordinating authority for AI and algorithm supervision and is expected to become the Dutch AI Act market surveillance authority. Given this role, its interpretation is likely to serve as a leading indicator. 

Singapore PDPC Publishes Guide on Federated Learning 

Singapore's Personal Data Protection Commission (PDPC) published a Guide on Federated Learning on July 20, 2026. The guide is intended to help organizations understand federated learning techniques and use cases, and navigate practical considerations for exploring and implementing federated learning as a Privacy Enhancing Technology (PET). The Guide is part of their PET Sandbox, which is intended for organizations to explore pilot use cases.  

China Finalizes Anthropomorphic AI Rules 

China’s Interim Measures for the Administration of Anthropomorphic AI Interaction Services took effect July 15, 2026. The final rule was jointly issued by five agencies (CAC, NDRC, MIIT, the Ministry of Public Security, and SAMR). It applies to AI services that provide continuous emotional interaction while simulating a natural person's personality traits, thinking patterns, or communication style. Ordinary smart customer service, Q&A tools, work assistants, education tools, and research tools are outside scope if they do not involve continuous emotional interaction. 

The final rules go beyond content moderation to add substantial user protection requirements: clear AI-human disclosure, dependency and addiction warnings, special protections for minors and older adults, limits on virtual intimate relationship services for minors, crisis-response obligations, user rights to copy and delete interaction data, and restrictions on using interaction data and sensitive personal information for model training without separate consent. Compliance obligations also include security assessments and algorithm filing. Potential penalties include fines of ¥10,000–100,000 for general violations, and ¥100,000–200,000 for violations involving harm to users' life or health safety. 

This is part of a broader China AI-governance push (IAPP). In May 2026, TC260 released the voluntary Ethics-Safety Guidelines for Artificial Intelligence Applications 1.0, effective July 1, 2026, which sets baseline expectations for AI developers, service providers, and users. Also in May, CAC, NDRC, and MIIT jointly issued the Implementation Opinions on the Standardized Application and Innovative Development of Intelligent Agents, effective July 15, 2026, which focuses on AI-agent oversight, authorization boundaries, traceability, risk controls, standards, and use cases. The AI agents document is structured as a policy implementation framework. It identifies 19 application scenarios and guides standards development, rather than directly imposing individual penalty provisions. Its specific compliance obligations will instead be implemented over time through sector-specific standards and filing requirements. 

Vietnam Issues List of High-Risk AI Systems 

On July 2, 2026, Deputy Prime Minister Ho Quoc Dung signed Decision No. 33/2026/WD-TTg, setting out the official list of high-risk AI systems, as outlined in the earlier Law on AI. The decision sets out the scope of application, criteria for identifying high-risk AI systems, responsibilities for implementation, and transitional provisions. The effective date of the decision is August 15, 2026. 

The annex attached to the decision lists designated kinds of high-risk AI systems, categorized by sector, and the kind of conformity assessment required as per the Law on AI. High-risk systems will either have to get a conformity certification before deployment, or suppliers may conduct their own conformity assessment or hire an external accredited vendor to conduct the assessment.   

The compliance date for AI systems in scope varies based on the sector. For any AI systems put into operation before August 15, 2026, AI systems in the healthcare, education, and finance sectors must be compliant before September 1, 2027. Any other AI systems in scope (in the ethnicity and religion, banking, litigation, and transportation sectors) that are put into operation before August 15, 2026, those systems must be compliant before March 1, 2027. For any other AI systems put into operation within six months of August 15, 2026, those systems must also be compliant before March 1, 2027.

Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security. 

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

What State Laws Require for Privacy Assessments

When are privacy assessments needed, and what must they cover?  State privacy laws have a lot to say about this, and state laws are taking different approaches for when assessments are needed and what they must cover. 

Why Organizations Do Privacy Assessments

Many privacy programs have processes to conduct privacy assessments of business activities.  These processes can be referred to by a lot of different names, like privacy threshold assessments, privacy impact assessments (PIAs), and data protection impact assessments (DPIAs).  Privacy programs may use the processes to serve different purposes, including to identify privacy requirements and risks, support data inventories and records of processing, or to document assessments when required by law. 

Having a privacy assessment process is a good starting point, but the process needs to be designed or tailored to address state law requirements if legal compliance is an objective.

What State Laws Require

In the U.S., state comprehensive privacy laws require a specific type of assessment to be conducted when certain triggers are met.  These triggers can include certain data processing activities, like those involving a "sale" of personal data, uses for targeted advertising, or certain profiling or automated processing.  Uses of certain types of personal data, like sensitive personal data or personal data relating to minors, can also trigger assessment requirements.  When they are required by state privacy laws, assessments generally need to be conducted and documented before the personal data processing starts--meaning before the product or feature goes live, advertising campaign launches, or vendor use starts.  They also must be updated before practices change.

State laws can also require assessments to cover specific questions or considerations that must be documented in the assessment.  There are some common elements that most states require, and there are unique requirements that only specific states require. 

For companies focused on privacy law compliance, it's important to conduct assessments when required, and to make sure the assessments address all required elements.  Documented assessments typically need to be provided to state regulators upon request, and companies subject to California's CCPA will ultimately need to make certifications to the state that assessments were conducted when required in 2026 (i.e., before in-scope personal data processing occurred).

The charts linked here have some high-level summaries of when assessments are required, and what they must cover, under state comprehensive privacy laws.  These include new assessment content requirements that Connecticut will require starting next month for certain profiling activities, and that Delaware's recently amended privacy law will require starting next year. 

How To Stay Compliant

If your organization hasn't reviewed and updated its privacy assessment processes in recent years, it may be time for a review.  Consider:

  • Validating policies and business processes require assessments before in-scope business activities launch

  • Refreshing training and guidance for business stakeholders on assessment processes

  • Tailoring assessment processes and platforms used so assessments are conducted (and not screened out) when state law triggers are met

  • Confirming all required questions and considerations are covered in the assessment

  • Sanitizing business stakeholder responses and information so documented assessments are ready for regulator review, and

  • Reviewing assessments and reassessing when activities change and when required by law.

Sam Castic is a Partner with Hintze Law, chair of the firm’s Retail Group, and co-chair of the Cybersecurity and Breach Response Group and FinTech + Financial Services Group. As a former chief privacy officer, he helps companies build, scale, and right-size privacy programs and strategies.

Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.

Texas App Store Law Now Enforceable Following SCOTUS Ruling: What App Developers Should Do

After months of uncertainty over whether and when Texas’s App Store Accountability Act (“Texas’s App Store Law”) would take effect, on the Supreme Court has ruled that it will not stand in the way of its enforcement while the Fifth Circuit considers constitutional challenges. The law which in part requires app stores to verify users’ ages and obtain parental consent to allow minors to download or purchase apps or to make in-app purchases and requires app developers to ingest those age signals is now in effect and enforceable.

Organizations subject to the law should be prepared to immediately comply or risk an enforcement action. Our analysis and recommendations are below.

As similar age-assurance laws in Alabama, California, Louisiana, and Utah now seem more likely to survive similar injunctive relief efforts and constitutional challenges, organizations should start preparing to comply with these laws as well. Look for our upcoming post comparing and contrasting the requirements under these other laws.

What did the SCOTUS decide and what happens next?

Texas’s App Store Accountability Act-- was set to take effect on January 1, 2026. The law was preliminarily enjoined from enforcement by a lower court on the basis that it likely violated the First Amendment under strict scrutiny. On June 1, 2026, the Fifth Circuit stayed the injunction pending its review, concluding that the law would likely survive intermediate scrutiny and that “The balance of equities and public interest are clearcut in Texas’s favor.” A trade group submitted an emergency request to the Supreme Court to vacate the stay. On Monday, July 6, 2026, the Supreme Court ruled, in a one sentence order, denying the request with the effect of making the law immediately enforceable.

While the law is still pending review by the Fifth Circuit for constitutionality challenges, those challenges seem less likely to prevail given the Fifth Circuit’s strong statements in favor of Texas in its prior ruling staying the injunction and the SCOTUS ruling supporting that stay. In the meantime, while the Texas State AG has not stated whether it will enforce the law immediately or wait for the Fifth Circuit to decide the constitutional issues, the AG may be emboldened to act more immediately given the Fifth Circuit’s supportive statements.

What are the requirements of Texas App Store Law?

The following summarizes requirements under the Texas App Store Law. While there are numerous requirements for app stores, we focus primarily on requirements for app developers.

Age and consent information ingestion and verification. The Texas app store law and similar state age-verification laws will require app stores to collect age information from account holders and for app developers to ingest age category data and status of parental consent from the app store and use it to verify age. Ingestion of age information that includes ages of children and minors triggers a complex set of obligations under other laws, including COPPA and state laws that apply if you have actual knowledge that someone is a child or a minor. The Texas Data Privacy and Security Act (TDPSA), in particular, is triggered if you gain actual knowledge of a child under 13 using your services. Under the TDPSA, data about a child is considered sensitive data and subject to requirements beyond those under COPPA, including requirements to conduct a data protection assessment.

Safe-harbor. The Texas App Store Law does not address what happens if an app developer has inconsistent information about age that it may have collected through its own age-gating process as compared to what it receives from an app store. But under the law, a software application has incentive to rely on the age of the app store as it is not liable for requirements to verify age if it has relied on the age category and consent information from the app store (and otherwise complies with the law). Relying on more robust means to determine age than the current self-declaration method used by many app stores (i.e., when a user simply states their age without confirming evidence) can create interesting issues for app developers. Further, many more app developers are relying on more robust means of age verification because UK regulators have recently advised against relying on self-declaration for age gating.

Age rating designation. App developers will need to assign age ratings to their apps, document the elements that led to that rating, and provide the rating and such elements to the app store.

Notice of significant changes. App developers will need to notify app stores about any significant changes to the terms of service or privacy policy of their application. App stores will in turn need to provide new notice and obtain new parental consent for any significant changes. A change is significant if it (1) changes the type or category of personal data collected, stored, or shared by the developer; (2) affects or changes the rating of the software application or the content or elements that led to that rating; (3) adds new monetization features to the software application, including: (A) new opportunities to make a purchase in or using the software application; or (B) new advertisements in the software application; or (4) materially changes the functionality or user experience of the software application.

Limits on use of age and consent information. App developers may only use age and consent information obtained from app stores to 1) enforce age-based restrictions in their application, 2) ensure compliance with laws and regulations, and 3) implement safety features and default settings. App developers may not share or disclose personal data of users obtained from the app stores in connection with the law.

What should app developers do?

  • Comply with Texas’s law. If you have not already, review the obligations under the app law to assess if and how it applies to your organization. Develop a strategy to quickly come into compliance.

  • Understand app store rules. Review (and have your engineers review) Apple (here and here) and Google’s (here) developer pages for information about how to ingest age information and how to provide age rating and related documentation. Both platforms have indicated they will only send signals in each state as they go into effect. Google has stated that they have begun rolling out their Play Age Signals API "for new users in Texas who created their accounts after May 28, 2026," while Apple describes its Declared Age Range API as available "in certain regions, where legally required."

  • Determine your strategy for ingesting age signals. Decide on whether you will ingest age signals for all states or just states with laws currently in effect (Google currently only makes Texas available where Apple appears to allow ingestion of age range for all states). In making this decision review and assess COPPA and Texas’ and other state laws that have obligations triggered by knowledge that a user is a child or a teen.

  • Formalize how you handle receiving age signals. Formalize processes for when you gain knowledge of users’ ages through these age signals or other means. Determine your strategy for compliance with laws triggered by knowledge of age and whether blocking, deletion, or obtaining parental or teen consent is appropriate under these laws.  

  • Consider your strategy for responding to conflicting age signals. If you currently age gate, you may receive conflicting information about age from app stores. Decide what approach you will use to resolve conflicting age signals. Evaluate the relative risks of your approach taking into consideration other state laws with clearer guidelines.

  • Get ready for additional laws set to take effect early next year. Although Texas  is the only state app store law currently in effect and enforceable, get ready for Alabama (January 1, 2027 - for new accounts after October 2, 2026; October 1, 2027, for accounts in existence on October 2, 2026) California (January 1, 2027), and Louisiana (July 1, 2027), and Utah (May 6, 2027).

Susan Hintze is the founder and co-managing partner of Hintze Law. Recognized by Chambers, Legal 500, & Best Lawyers, Susan serves on the International Association of Privacy Professionals (IAPP) Board of Directors and is an IAPP Westin Emeritus Fellow. She is also co-chair of the firm’s Regulatory Defense Group.

Emily Litka Sanford is a Senior Associate at Hintze Law. Emily focuses her practice on global privacy and emerging AI laws and regulations.

Hansy Piou is an Associate at Hintze Law. Hansy has experience with global data protection issues, including kids’ global privacy laws, AADC, privacy impact assessments, GDPR, and privacy statements.


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on privacy, data security, and AI law. Its attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of privacy, data security, and AI law. 

More Companies Are in Scope for State Data Broker Laws 

By Sam Castic

New and amended data broker laws make more companies that collect and disclose personal data subject to state data broker laws.  Last week New Jersey enacted a unique new data broker and data collector law, and Connecticut enacted (and then amended) one last month.  With Vermont's recent expansion of its law, and California regulation changes that took effect this year, there are some emerging scope expansions for these laws that all companies that collect and disclose personal data should be aware of. 

Read More

Hintze and Partners Recognized in SuperLawyer and Legal 500 Rankings

Alex Schlight and Taylor Widawski Named to 2026 Rising Stars

We are pleased and excited to announce that Partners Taylor Widawski and Alex Schlight at Hintze Law PLLC, were selected to the 2026 Super Lawyers Rising Stars list, an honor reserved for top-rated attorneys demonstrating exceptional professional achievement and impact. The Rising Stars list recognizes no more than 2.5 percent of attorneys in each state.

For both Alex and Taylor, their continued recognition (2024–2026) reflects not only sustained excellence, but also their leadership as trusted advisors at the forefront of artificial intelligence, privacy, and technology law.


Taylor Widawski: Practical, Scalable Privacy and AI Strategy

Taylor Widawski, a Partner at Hintze, serves as co-chair of the firm’s Artificial Intelligence and Machine Learning Group and FinTech + Financial Services Privacy Group. Her inclusion in the 2026 Rising Stars list reflects her ability to translate complex regulatory regimes into clear, actionable guidance for clients.

Taylor’s practice focuses on:

  • Supporting AI product development and privacy-by-design initiatives

  • Advising on major U.S. privacy laws, including CCPA/CPRA, VCDPA, CPA, and UCPA

  • Counseling on global frameworks such as the GDPR

  • Leading vendor risk management and contract negotiations

  • Conducting privacy impact assessments and program development

  • Guiding post-M&A privacy integration efforts

Her prior in-house roles at T-Mobile and Chime Financial, along with secondment experience at a leading social media company, give her a practical, business-oriented perspective. She is particularly valued for her ability to collaborate with cross-functional teams and provide scalable solutions in uncertain regulatory environments.

Alex Schlight: Leading at the Intersection of Workplace Privacy and AI

As a Partner at Hintze and co-chair of the firm’s Workplace Privacy Group and Artificial Intelligence and Machine Learning Group, Alex Schlight has built a reputation for delivering precise, forward-thinking counsel on data privacy and AI governance.

Alex advises U.S. and international clients on privacy compliance and risk management strategies, with a practice that includes:

  • Developing privacy and AI policies and programs

  • Drafting and negotiating data protection agreements

  • Conducting privacy-by-design reviews

  • Supporting risk assessments and mitigation strategies

  • Managing data subject request processes

Her experience spans industries including SaaS, AI, e-commerce, life sciences, AR/VR, and data analytics, and ranges from startups to Fortune 100 companies.

Notably, her in-house perspective, gained through secondments and work with leading technology and social media companies, enables her to deliver advice that is both strategic and operationally practical.

Senior Partners Recognized in Super Lawyers List

We are also proud to share that Partners Susan Hintze and Mike Hintze have once again been selected to the 2026 Super Lawyers list, recognizing their exceptional leadership and long-standing excellence in privacy, data protection, and cybersecurity law. This continued recognition reflects not only their deep subject-matter expertise but also their trusted role advising organizations on some of the most complex and evolving legal and regulatory challenges. Their inclusion underscores Hintze Law’s commitment to delivering strategic, practical counsel at the forefront of privacy and AI.

Susan has also been recognized this year as a Lexology Index Thought Leader and in the 2026 Lawdragon 500 Leading Global Cyber Lawyers.


Legal 500 Rankings Live and Team Hintze Ranks Once Again

Hintze has also been recognized by The Legal 500 in its United States Cyber Law (including data privacy and data protection) rankings as a notable ranked firm, distinguishing itself as a boutique practice in a field largely dominated by large, full-service law firms. The firm is highlighted for its exclusive focus on AI, privacy, and data security legal counseling, advising a broad range of clients, from major multinational companies to emerging technology startups, on complex regulatory compliance, data governance, and cybersecurity issues. Client feedback referenced in the rankings emphasizes the firm’s practical, business-oriented advice and its ability to leverage cross-industry experience to guide organizations through evolving regulatory landscapes.


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Law Global AI Legal Updates 

Hintze Law’s Global AI Update provides a curated overview of key AI-related legal and regulatory updates. We spotlight new developments and emerging trends to help organizations that are developing, deploying, or relying on AI technologies to stay ahead of what’s next. 

Please also check out our latest Global Privacy Updates post. 

If you’d like to receive email alerts for our blog posts, visit our blog page to sign up. 


U.S. Updates 

Trump Signs EO Promoting Advanced AI Innovation and Security  

On June 2, 2026, the U.S. president signed an Executive Order ("EO") titled "Promoting Advanced Artificial Intelligence Innovation and Security." The EO focuses on three main areas: directing the U.S. Attorney General to prioritize enforcement against individuals utilizing AI in criminal contexts, establishing a classified federal benchmarking process and voluntary developer framework to secure “covered frontier models,” and expanding AI-driven cybersecurity efforts across federal agencies. While the enforcement priority is indefinite, most of the other agency directives require completion within 30 to 60 days. 

Connecticut Enacts Broad Online Safety and AI Law 

On May 29, 2026, Connecticut enacted SB 5, a multi-faceted AI law that draws from a number of types of AI laws throughout the country with varying requirements in specific contexts.  

Among the provisions, the law includes requirements related to AI transparency for subscription-based AI, documentation and notice obligations for automated decision-making in employment, and provenance-data labeling for large-scale generative AI providers. Additionally, it establishes whistleblower protections for employees of frontier AI developers, sets requirements for companion chatbots, and mandates age verification and data-privacy controls for social media platforms that recommend content to minors. 

Many provisions will be enforced as unfair or deceptive trade practices, heightening compliance risk and signaling increased enforcement activity across AI and online safety domains.  

Provisions in the law become effective between October 1, 2026, and January 1, 2028. 

Illinois postpones regs on AI notices in Employment Contexts 

On June 2, 2026, the Illinois Department of Human Rights (“IDHR”) announced that it is temporarily postponing proposed rules related to AI notice requirements in employment decisions. 

The IDHR was set to hold a public hearing on June 10, 2026, regarding draft regulations implementing the Artificial Intelligence in Employment Provisions of the Illinois Human Rights Act. The act includes transparency and notice requirements for employers using artificial intelligence and automated decision-making systems in hiring and employment. The draft regulations provided details of when, how, and where AI notices are required and what they must contain. The announcement did not state when the hearing would be rescheduled for nor did it mention whether there would be changes to the draft regulations. 

Colorado Enacts Companion Chatbot Law 

On June 1, 2026, Colorado enacted a law to regulate AI companion chatbots. Among its provisions, the law requires: age estimation; AI disclosure requirements; design limits, content restrictions, and safety measures for minors; specific account tools related to privacy and account operations; protocols for responding to user expressions of suicidal ideation or self-harm; and annual reporting obligations to the Attorney General. The law also forbids chatbots from representing their outputs as equivalent to advice from licensed professionals. The law is enforceable by the AG’s office and will take effect on January 1, 2027. 

Florida Sues Open AI 

On June 1, 2026, and during an ongoing criminal investigation by the Florida AG against Open AI, Florida AG Uthmeier announced a civil lawsuit against Open AI under the Florida Deceptive and Unfair Trade Practices Act (“FDUTPA”) and common law causes of action. The complaint alleges OpenAI knowingly deployed an unsafe AI product, ignoring internal and external safety warnings and exposing users, including children, to harm. According to the Attorney General, ChatGPT allegedly collected data from minors without meaningful parental oversight, created risks of behavioral addiction and cognitive harm, and produced dangerous or misleading outputs that were downplayed by the company.  

The lawsuit seeks civil penalties, damages, and injunctive relief requiring changes to OpenAI’s practices. The civil action follows an ongoing criminal investigation into whether ChatGPT played a role in the planning and commission of violent crimes. 

Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.
Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze & Partners Recognized by Chambers in 2026 USA Rankings

Hintze Law PLLC is pleased to announce that the firm and its attorneys have once again been recognized by Chambers & Partners for excellence in Privacy & Data Security in the 2026 Chambers USA Guide.

These rankings reflect continued recognition from clients, peers, and industry stakeholders for the firm’s work advising organizations on complex data protection challenges in an increasingly regulated and technology-driven economy. As privacy and data security laws continue to evolve at the federal, state, and global levels, these rankings underscore the firm’s role in helping clients navigate compliance obligations while supporting business growth and innovation.

Firm Recognition

Hintze Law has been ranked once again in the Privacy & Data Security: The Elite (USA Nationwide) category, placing the firm among a select group of practices recognized for their leadership and depth of experience in privacy and data security law.

Clients and Chambers alike tout Hintze Law’s “experts who are in-house experienced advisers and a fantastic client base that enables them to benchmark. They are able to distil complex matters into tangible and proportionate steps.”

According to Chambers, clients value the firm’s capabilities, noting:

“Hintze Law is a highly regarded boutique firm, particularly noted for its experience in handling cutting-edge technology and emerging issues impacting information security, such as automatic tracking, biometrics and facial recognition. The law firm is well versed in establishing compliance regimes in addition to responding to data breaches and ensuing investigations.”

This feedback reflects the firm’s broader approach of integrating legal analysis with real-world business considerations, particularly for clients navigating rapidly evolving privacy requirements.

Strength in Healthcare and Data-Driven Industries

The firm was also ranked in the Privacy & Data Security: Healthcare – USA category. Chambers notes Hintze Law’s experience “is highly regarded by healthcare and biotech clients for advising on relevant data privacy and security laws such as HIPAA and COVID-19 pandemic responses and monitoring,” and data protection frameworks, as well as supporting digital health, biotechnology, and data analytics organizations.

This work increasingly intersects with broader issues involving artificial intelligence, machine learning, and large-scale data processing, where healthcare and life sciences companies are navigating both innovation and regulatory complexity.

Individual Rankings

Chambers & Partners has again recognized Susan Hintze, Mike Hintze, and Sam Castic in the Privacy & Data Security: Privacy (USA Nationwide) category.

Susan Hintze is the Founder and Co-Managing Partner at Hintze Law PLLC. She serves on the International Association of Privacy Professionals (IAPP) Board of Directors and is an IAPP Westin Emeritus Fellow, and she is also co-chair of the firm’s Regulatory Defense Group. Susan was ranked in both the Privacy & Data Security: Privacy (USA – Nationwide) category and the Privacy & Data Security: Adtech (USA – Nationwide) category, and she continues to be recognized in the 2026 Chambers Global Guide.


The Chambers review notes Susan “is particularly sought after for her expertise in the interplay of cutting-edge technology with data security regulations.”

Mike Hintze is a Member Partner at Hintze Law PLLC, chair of the firm’s Health and Biotech Privacy Group, and a recognized leader in privacy and data protection law, policy, and strategy.

Mike was also ranked in the Privacy & Data Security: Adtech (USA – Nationwide) and Privacy & Data Security: Privacy (USA – Nationwide) categories, and is also ranked in the 2026 Chambers Global Guide.  Chambers noted that Mike “is highly regarded for his top-level experience of in-house data security in the technology sector, which he brings to private practice.”


Sam Castic is a Partner at Hintze Law, chair of the firm’s Retail Group, and co-chair of the Cybersecurity and Breach Response Group and FinTech + Financial Services Group.

Sam was ranked once again in the Privacy & Data Security: Privacy (USA - Nationwide) category while also being recognized in the 2026 Chambers Global Guide.  Chambers noted that Sam “is highly regarded for his practical strategies regarding privacy programs, data processing and security, AI and transfer agreements. He counsels clients from a range of sectors including, retail, e-commerce, technology, social media and fintech.”


Their continued inclusion in the rankings reflects longstanding recognition of their leadership in the field and their ability to advise clients on both strategic and operational privacy and data security challenges and opportunities. Their experience spans regulatory counseling, enforcement matters, and the practical implementation of privacy programs within organizations.

Continued Recognition Across Global Rankings

The firm’s continued recognition in the 2026 Chambers USA Guide builds on its inclusion in the 2026 Chambers Global Guide, where Hintze Law was ranked for the fifth consecutive year as an Elite firm for Privacy & Data Security and for the third year in Privacy & Data Security: Healthcare.  Susan Hintze, Mike Hintze, and Sam Castic were also recognized in the 2026 Chambers Global Guide.  For more information about the Global Guide rankings, see our blog post.

These global rankings highlight the firm’s work and reputation supporting global organizations on privacy and data security matters.

Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security.
 

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Law Global Privacy Updates 

The Hintze Law team continues to monitor global privacy and data security developments to provide timely, practical insights for clients. Below is a summary of key updates from late May through early June 2026. For developments in AI, please see our latest Global AI Updates. 


US Privacy Updates 

California Regulators Secure $12.75 Million GM Privacy Settlement 

On May 6, 2026, the California AG and county district attorneys announced a $12.75 million proposed settlement with General Motors (GM) and OnStar for alleged violations of the California Consumer Privacy Act (“CCPA”) and other California state laws. The AG alleged that GM sold California residents’ driving and location data to data brokers, even though it said it did not sell personal information and that it retained driving and location data long after being used to operate OnStar’s connected vehicle services, making it one of the first actions to focus on data minimization. 

The settlement requires GM to obtain consent before disclosing certain driving data to third parties, to delete certain driving data within 180 days of collection, and to allow customers to disable collection of precise geolocation data from vehicles. Earlier this year, GM & Onstar settled with the FTC (see our blog post by Elizabeth Crooks and Susan Hintze) for similar allegations. The Iowa AG’s office has also filed suit against GM & OnStar making related claims (See our summary in our March Global Privacy Updates post). 


Utah Imposes Liability for Platforms Hosting Material Harmful to Minors 

On May 6, 2026, amendments to Utah’s age verification law (S.B. 73 and Title 78B-3 Part 10, respectively) took effect, imposing obligations on publishers and distributors of material deemed harmful to minors and reiterating the state Division of Consumer Protection’s enforcement authority with respect to the law. 

Utah’s age verification law has required age verification and prohibited facilitating circumvention methods such as VPN use, enforced by the Division directly under the law, since 2023. Now, entities may face liability under a private right of action where minors access restricted content or where identifying information collected for age verification is retained improperly. The Division is also now authorized to administer and enforce the law as part of its general jurisdiction, which includes guidance and investigatory powers. 

The Division is expected to provide additional guidance on compliance standards, including age verification methodologies and scope determinations. 


Vermont Enacts Neurological Rights Law 

On May 18, 2026, Vermont enacted H. 814, establishing statutory protections related to neurological data and AI use in health and human services. The law took effect upon being enacted. 

The law grants individuals rights related to mental privacy, freedom of thought, and protection from unauthorized neurotechnological interference. It also mandates further study and reporting by the state’s AI Advisory Council.  

This development signals increasing legislative attention to emerging risks associated with neurotechnology and AI-driven cognitive data processing. 


Louisiana Advances Comprehensive Privacy Law 

Signed by the governor on May 29, 2026, Louisiana’s Data Privacy Act establishes a comprehensive privacy framework similar to other state laws.  

The law provides consumer rights, including access, deletion, and opt-out rights, and imposes obligations such as data minimization, purpose limitation, disclosure of sale of sensitive or biometric data, and data protection assessments for high-risk processing. Notably, an entity that does business in Louisiana that “derives fifty percent or more of its annual revenues from selling consumers' personal information” needs prior consumer consent before selling their sensitive data. 

The law takes effect January 1, 2027, with enforcement by the state attorney general and a temporary cure period.  


Connecticut Enacts Data Broker Law 

On May 27, 2026, the governor of Connecticut signed into law An Act Concerning Consumer Privacy and Protection (SB4). The law primarily applies to data brokers, defined as any business that sells or licenses “brokered personal data” to another person, where such data is defined as personal data elements categorized or organized for sale or license to a third party. Such data elements include name, address, date of birth, and other information that, alone or in combination with the other information sold or licensed, would allow a reasonable person to identify the consumer. Subject to further rulemaking, SB4’s provisions require data brokers to register and comply with a Department of Consumer Protection provided deletion request platform. 

On June 2, 2026, the governor signed HB5222. The law modifies SB4 by exempting personal data in compliance with the Driver's Privacy Protection Act, exempting a covered entity, business associate or protected health information under HIPAA from the data broker requirements, and changing the civil penalty to up to $200 per day per consumer for each violation of the data broker requirements. 

SB4 enters into effect on October 1, 2026. The data broker registration requirement enters into effect on January 1, 2027, with other requirements entering into effect in the following years. 


Connecticut Amends Connecticut Data Privacy Act   

On June 2, 2026, the governor signed HB5222, which amends the Connecticut Data Privacy Act to expand deletion rights to apply to certain “publicly available information” and inferences from such data, prohibit the sale of precise geolocation data, and add other provisions, starting October 1, 2026. 

Although “publicly available information” is not personal data under the Connecticut Data Privacy Act (CTDPA), HB5222 excludes a number of types of personal data from the definition and expands it in one aspect to include data obtained from widely distributed media (e.g., public sources). It also narrows the definition to exclude public information that's combined with other personal data types, and potentially personal data accessible on a website where the consumer restricted access to a specific audience (which some companies or data brokers may scrape believing it to be public data). 

HB5222 enacts new obligations for businesses using facial recognition technology on their premises, where such technology analyzes facial features in still images or video to uniquely and personally identify a specific individual. The edits narrow the CTDPA's statutory exceptions for controllers or processors that use such technology for security, fraud prevention, or to help prevent or respond to illegal activity, including by prohibiting use of third-party databases to help with identity matching, requiring signage at each premises entrance, and mandating a publicly disclosed facial recognition technology policy. 


Connecticut Enacts Surveillance Pricing Law 

On June 2, 2026, Connecticut enacted a surveillance pricing law as a part of HB5222 which takes effect February 1, 2027.  Surveillance pricing under the law includes establishing a customized price for a consumer good or service that is based (in whole or part) on personal data collected (A) through any technology or technological method, and (B) by the person establishing the customized price either directly or indirectly. The law prohibits surveillance pricing by certain retailers and third-party delivery services. 

Companies engaging in surveillance pricing for online transactions may be required to prominently display in advertising, and price listings, a notice that “THIS PRICE WAS INCREASED USING YOUR PERSONAL DATA” if the surveillance pricing didn’t result in a discount. 


Stay on Enforcement of Texas App Store Law Lifted 

On May 28, 2026, the Fifth Circuit Court of Appeals lifted the preliminary injunctions that blocked enforcement of Texas’s App Store Accountability Act. Since it was set to take effect January 1, 2026, the Attorney General can now enforce the Act while constitutional challenges to the Act remain ongoing. 

Obligations for app developers include designating age ratings for each app based on its content/elements, notifying app stores of significant changes, and verifying ages and parental consent status using information from app stores. 


State Enforcement Focuses on Children’s Privacy and Platform Design 

State AGs continue to pursue enforcement actions targeting platform practices allegedly affecting minors. 

  • Texas filed suit against Netflix alleging deceptive practices related to user data collection and advertising representations.  

  • Oklahoma filed lawsuits against Roblox and Temu alleging inadequate protections for minors and unlawful data collection practices.  

  • Texas also sued Discord, alleging insufficient age verification and misleading safety representations.  

These actions reflect an ongoing enforcement priority on age verification, transparency, and alignment between public representations and actual data practices.  


Texas Expands Enforcement on Consumer Data Practices 

Texas regulators continue to pursue enforcement and investigations involving consumer data. 

  • On May 11, 2026, the Texas attorney general announced a settlement with LG requiring enhanced consent and disclosure practices for viewing data collection.  

  • On May 20, 2026, the attorney general launched an investigation into Meta’s AI-enabled smart glasses, citing concerns regarding continuous data capture and transparency.  

These actions underscore increasing scrutiny of connected devices and AI-enabled data collection technologies. 


Louisiana Adopts App Store Age Verification Framework 

On May 15, 2026, Louisiana enacted HB 977, establishing requirements for app stores and developers to verify user age and obtain parental consent for minors.  

The law creates shared obligations across app store operators and developers, including data-sharing requirements and enforcement mechanisms overseen by the attorney general. These requirements enter into effect on July 1, 2027. 

The framework reflects a broader trend toward ecosystem-wide accountability for child privacy compliance. 


EEOC Considers Rescinding Demographic Reporting Requirement 

On May 14, 2026, the U.S. Equal Employment Opportunity Commission submitted a proposal to the Office of Information and Regulatory Affairs rescinding the requirement for large employers to submit annual demographic reports.  

If finalized, employers may need to reassess data collection practices in light of other applicable legal obligations and operational needs. 


Beyond US Updates 

European Commission Finds Potential DSA Violations by Meta 

On April 29, 2026, the European Commission announced preliminary findings alleging that Meta violated the Digital Services Act by failing to adequately prevent underage access to its platforms.  

The Commission claimed deficiencies in Meta’s age verification mechanisms and platform safeguards. The Commission also states it is continuing to investigate other potential DSA breaches by Meta, including Meta’s assessment and mitigation of risk of “addictive behavior” of minors driven by online features. . 


Canada Issues Guidance on Age Assurance 

Canada’s Office of the Privacy Commissioner issued guidance outlining when and how organizations should implement age assurance mechanisms.  

In its Policy Note, the Office of the Privacy Commissioner noted that no singular age assurance method has been broadly adopted across Canada, and while its position regarding such a method may change, the office emphasized that age assurance is one part of a children safety program. The guidance emphasizes proportionality, risk-based implementation, and limits on the use of collected data, reinforcing privacy-by-design principles. 


Turkiye Regulates Social Media and Gaming Platforms 

On April 22, 2026, Turkiye adopted amendments to Law No. 5651 imposing age-based restrictions and parental control requirements for social media and gaming platforms.@ 

The amendments require age verification, service restrictions for minors, and enhanced parental oversight tools, aligning with global trends toward increased protections for children online. 


Latvia Issues Cookie Compliance Guidance 

On May 8, 2026, Latvia’s Data State Inspectorate released guidance identifying common deficiencies in cookie consent practices.  

The guidance reiterates the requirement for clear, informed, and freely given consent, as well as functional user controls and transparent disclosures. 


Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on AI, privacy, and data security. Hintze attorneys and data consultants support technology, ecommerce, advertising, media, retail, healthcare, and mobile companies, organizations, and industry associations in all aspects of AI, privacy, and data security 
 

Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze

Hintze Law Global AI Legal Updates

Hintze Law’s Global AI Update provides a curated overview of key AI-related legal and regulatory updates. We spotlight new developments and emerging trends to help organizations that are developing, deploying, or relying on AI technologies stay ahead of what’s next.

Please also check out our latest Global Privacy Updates post.

If you’d like to receive email alerts for our blog posts, visit our blog page to sign up.

U.S. Updates

CA Governor Issues Executive Order Responding to Economic Disruption Due to AI

On May 21, 2026, California Governor Gavin Newsom announced a first-of-its-kind executive order targeted at responding to the impact of AI on California's workforce. The order is directed to various state agencies and appears designed to (1) mitigate further AI-caused worker disruption and (2) restore worker power resulting from past disruptions related to AI.

While this is the first state EO to address AI-caused worker disruption, it covers many of the same topics as the government-focused provisions in Connecticut's recent omnibus law (SB 5), such as providing resources for workers displaced by AI, incorporating AI as a possible cause in labor market analyses, and partnering with institutions of higher education to understand the harms and risks AI poses to the workplace.

The EO requires several reports, recommendations, and similar output from different state agencies by the end of 2026, so it is likely there will be follow-up legislative action based on those outputs over the next couple of years.

Colorado Advances Replacement for 2024 AI Act

On May 14, 2026, Colorado passed Senate Bill 26-189, which would repeal and replace the state’s existing 2024 AI Act.

The law narrows former concepts of “high-risk artificial intelligence system” and “algorithmic discrimination” to instead cover “automated decision-making technologies” (ADMT), defined broadly to include systems that process personal data to produce outputs such as predictions, classifications, rankings, or recommendations that influence decisions affecting individuals. Under the new law, these ADMT systems are regulated only when used in “consequential decisions,” including those related to employment, housing, education, lending, insurance, health care, and government services.

The law scales back certain obligations found in the original Act, including removing risk management and impact assessment requirements, while maintaining transparency obligations.

The bill also imposes distinct duties on developers and deployers. Developers must provide detailed disclosures regarding intended use, known risks, and training data, as well as instructions for appropriate use and oversight. The law maintains the requirement to retain compliance records for at least three years. Deployers are subject to disclosure obligations, recordkeeping requirements, and post-decision transparency where AI contributes to adverse outcomes.

Consumers are granted new rights, including the ability to correct inaccurate data and request meaningful human review of AI-influenced decisions. These requirements are subject to further attorney general rulemaking.

Enforcement authority remains with the Colorado Attorney General. The law will take effect on January 1, 2027.

Georgia New AI Companion Chatbot Law

On May 11, 2026, Georgia enacted SB 540, a law requiring operators of AI companion chatbots - systems designed to simulate ongoing, personalized human-like relationships - to disclose their AI nature to users at the start of each session and periodically throughout, implement parental controls and age verification, provide privacy tools, and adopt protocols for responding to suicidal ideation or self-harm.

The law carves out customer service bots, internal business tools, and educational applications, but contains no exemption for chatbots embedded within larger platforms.

The Attorney General may pursue civil penalties of up to $10,000 per knowing violation per affected user per day. The law takes effect July 1, 2027.

Iowa Expands Companion AI Chatbot Regulation

On May 3, 2026, Iowa passed  Senate File 2417, a law regulating AI companion technologies. The law applies to operators providing conversational AI platforms—those accessible to the general public and that have the primary purpose of simulating human conversation and interaction through textual, visual, or aural communication.

Iowa’s law requires operators to inform users they are interacting with AI. The law also includes safety controls for known minors, parental controls for users under 13, and protocols for responding to user expressions of self-harm.

The attorney general has sole enforcement authority of the law, with no private right of action. The law takes effect on July 1, 2027

Hawaii Enacts Companion AI Disclosure and Safety Requirements

On May 6, 2026, the Hawaii legislature passed the Artificial Intelligence Disclosure and Safety Act (SB 3001, CD1). The bill is now awaiting the governor’s signature. The bill focuses on AI companion services and introduces both transparency and safety obligations.

If signed into law, operators would be required to clearly disclose that users are interacting with AI systems rather than human beings. Where the operator knows or reasonably believes a user is a minor, disclosures must be more prominent and frequent. Operators would also be required to implement protocols to respond to user expressions of self-harm or suicidal ideation, including directing users to crisis support services. AI systems would also be prohibited from representing themselves as licensed mental health professionals. Beginning January 1, 2028, operators will be required to submit annual reports detailing safety protocols and the number of crisis-related interventions.

Enforcement authority rests with the Hawaii Attorney General, and violations may result in civil penalties. The law does not provide a private right of action.

Nebraska Passes Companion AI Chatbot Law

On April 14, 2026, Nebraska passed the Conversational Artificial Intelligence Safety Act. The law mandates clear disclosure provisions, including specific transparency and safety requirements for interactions involving minors. Operators are required to establish protocols for responding to user expressions of self-harm. The law also prohibits chatbots from representing themselves as professional mental or behavioral health care providers.

The law takes effect on July 1, 2027, with enforcement handled by the Attorney General and civil penalties of at least $1,000 per violation.

Florida AG Opens Investigation into OpenAI/ChatGPT

On April 9, 2026, Florida Attorney General James Uthmeier announced that his office had opened a formal investigation into OpenAI and its product ChatGPT, stating that subpoenas to the company would be issued.

Uthmeier said the investigation was prompted by information indicating that ChatGPT may have been used by the perpetrator of a mass shooting at Florida State University. Uthmeier also cited additional concerns regarding child safety, alleged encouragement of self-harm, and questions about OpenAI's data practices and national security implications, especially regarding links to China.

Maryland Passes Algorithmic Pricing Bill

On April 28, 2026, Maryland passed into law HB 0895. The law will apply to “food retailers” (e.g., grocery stores) as well as “third-party deliver service providers” (e.g., consumer food delivery services).

Regulated entities will be subject to the following requirements for Maryland consumers:

  • No personalized pricing: Must not engage in “dynamic pricing” or otherwise use any “personal data” to set a higher price for tax-exempt food with respect to a given consumer.

    • “Dynamic pricing” means setting personalized prices for goods/services for a given consumer based on that consumer’s personal data.

    • “Personal data” has the same meaning as in MODPA.

  • Limited use of sensitive data: Must not use “protected class data” about a given consumer to offer, advertise, or sell consumer goods or services to that consumer, where doing so would have a detrimental effect to that consumer not experienced by others

    • “Protected class data” means “information about an individual or group of individuals that, alone or in combination, directly or by implication identifies a characteristic… legally protected from discrimination under [state or federal law].”

The law grants regulated entities a 45-day right to cure. Enforcement will be exclusive to the MD Division of Consumer Protection as a violation of the state’s consumer protection act. The bill takes effect on October 1, 2026.

Maine Moves to Limit AI in Mental Health Care

On April 13, 2026, Maine signed into law HP 1397, an act restricting use of AI in relation to therapy or psychotherapy services provided to Maine residents:

  • Only licensed professionals may use “Internet-based” AI to provide, advertise, or otherwise offer these services to the public.

  • Licensed professionals must not “allow” AI to make independent therapeutic decisions, directly interact with clients as part of therapeutic communications, or generate therapeutic recommendations or treatment plans that they do not review and approve. Additionally, licensed professionals may use AI for administrative support (e.g., billing) or supplementary support (e.g., taking notes) only if they:

1.      Use AI in accordance with standards of practice and applicable law (including privacy laws),

2.      “[M]aintain[] full responsibility for all interactions, outputs[,] and data use associated with the [AI] use,” and

3.      If using for supplementary support, obtain the client’s informed consent, and record/transcribe the client’s sessions that use AI.

Clients cannot waive these requirements, and the law does not preclude PRAs based on a licensed professional’s use of AI. Rulemaking is required by the oversight boards for regulated professionals. This law takes effect July 14, 2026.

Vermont Governor Approves Bill on Neurological Rights and Use of AI Tech in Health

On May 18, 2026, Vermont signed into law H. 814, an act relating to neurological rights and the use of artificial intelligence technology in health and human services. The law provides for the recognition that each individual has neurological rights, including "mental and neural data privacy," “nondiscrimination in the development and application of neurotechnologies,” and protections to unauthorized neurotechnological interventions.

The law also modifies the membership of Vermont's AI Advisory Council and requires the Council to submit a written report about AI and neurological rights, including any statutory recommendations, by January 15, 2027.

X Fails to get Preliminary Injunction on AB 2013

On March 4, 2026, a US District Court denied, preliminary injunction against CA AB 2013 sought by xAI, the AI company developing X’s chatbot. The law requires developers of generative AI to make public disclosures about the training data behind their GenAI products.

The court found that xAI’s allegations that the disclosure requirement would force xAI to disclose valuable trade secrets to be vague, where xAI pointed to the value of secrecy in data sets, but did not “describe the subject matter of the trade secret with sufficient particularity” to distinguish xAI’s use from its competitors and warrant trade secret protection.

Senate Releases Draft of Trump America AI Act

On March 18, 2026, Senator Marsha Blackburn (R-MO) announced a draft bill titled the TRUMP AMERICA AI Act which is intended to establish a federal standard on AI and override state efforts on legislating AI.

Provisions under the proposed law cover youth online privacy and safety, AI property and likeliness rights, and AI innovation. The bill if enacted would preempt conflicting state laws but would allow state laws to provide greater protection for minors.

The bill has no private right of action and would be enforceable by the US AG and state AGs

National Policy Framework for AI

On March 20, 2026, the Trump White House announced its National Policy Framework for Artificial Intelligence. The framework addresses six key objectives: 

  • "Protecting Children and Empowering Parents"

  • "Safeguarding and Strengthening American Communities"

  • "Respecting Intellectual Property Rights and Supporting Creators"

  • "Preventing Censorship and Protecting Free Speech"

  • "Enabling Innovation and Ensuring American AI Dominance"

  • "Educating Americans and Developing an AI-ready Workforce"

  • “Establishing a Federal Policy Framework, Preempting Cumbersome State AI Laws”

The press release emphasized the need for uniformity in AI regulation across the states, warning that “a patchwork of conflicting state laws would undermine American innovation and our ability to lead in the global AI race."

Additional AI Legislation Passed

In addition to the laws discussed above, the following laws have been enacted since our last update:

·       New York S 8828 – Requiring transparency and safety requirements for AI frontier models

·       Oregon SB 1546 - Regulating Companion Chatbots

·       Tennessee SB 1580 – Prohibiting AI systems from being advertised or represented as qualified mental health professionals 

·       Washington HB 2225 – Regulating Companion Chatbots

·       Washington HB 1170 – Requiring Transparency for AI Generated / Altered Content

·       Washington SB 5395 – Requiring human responsibility and determination for medical necessity and authorization

·       Washington SB 5886 – Protecting against forged digital likeness

·       Washington SB 5105 – Prohibiting AI-generated sexually explicit depictions of minors


Global Updates

European Commission Publishes Guidelines for Use of GenAI in Research

On May 8, 2026, the European Commission announced updates to Guidelines on the European Research Area's use of GenAI in research. The guideline’s provisions for researchers, research organizations, and research funding organizations include:

  • Maintaining responsible for the integrity of scientific output

  • Using GenAI transparently

  • Refraining from substantially using GenAI in sensitive activities that could impact other researchers or organizations, such as peer review and evaluating research proposals 

India Finalizes Amendments Targeting “Synthetic Information”

The Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Amendment Rules, 2026, have now entered into effect, updating India’s 2021 IT Rules. A key focus of the amendments is “synthetically generated information” (SGI)—content generated to appear real, authentic, or true, and that may be indistinguishable from real individuals or events.

The amendments introduce a structured compliance framework for intermediaries that enable the creation or dissemination of such content. Intermediaries are now required to notify users at least once every three months of their obligations relating to SGI. Where violations occur, intermediaries must take swift action, including removal of unlawful content within three hours of notice.

The rules also impose more prescriptive technical requirements. Platforms must deploy safeguards designed to prevent the creation and dissemination of unlawful SGI, while explicitly prohibiting certain high-risk categories. For permitted synthetic content, mandatory labeling and provenance requirements apply, including embedding of identifiers to signal that content is synthetic. In addition, the amendments include safeguards to prevent tampering with or removal of such labels and metadata—highlighting a growing regulatory emphasis on traceability and authenticity in AI-generated content.

U.K. ICO Focuses on AI and Automated Decision-Making in Recruitment

The U.K. Information Commissioner’s Office (ICO) continues to sharpen its focus on the use of AI and automated decision-making (ADM) in hiring. Between March 2025 and January 2026, the ICO engaged with more than 30 employers to better understand how automation is being used in recruitment decision-making.

In March 2026, the ICO published its findings in its report, Recruitment Rewired: An Update on the Fair and Responsible Use of Automation in Recruitment. The report outlines regulatory expectations for employers deploying AI tools in hiring processes, particularly around fairness, transparency, and accountability. ICO states in its report that recruitment remains a key enforcement priority, especially where automated systems materially influence hiring outcomes.

Pope Leo XIV Approves Interdicasterial AI Commission and Publishes Encyclical On AI

On May 12, 2026, Pope Leo approved the creation of a Interdicasterial Commission on Artificial Intelligence. The statement “serves as food for thought and does not intend to contradict work conducted in existing G7 groups such as the Hiroshima AI Process.”

On May 25, 2026, the Pope published his first encyclical, Magnifica humanitas: On Safeguarding the Human Person in the Time of Artificial Intelligence. Breaking tradition, the Pope was reported to attend the encyclical’s launch, along with one of the Anthropic co-founders.

The encyclical outlines the Catholic Church’s perspective on the care of human dignity in the era of AI, rooted in the Church’s principles of Social Doctrine, including the common good and social justice. From these principles, Pope Leo urges the discreditation of the assumption that “technical power automatically confers the right to govern,” maintaining as truth as a common good, and protecting freedom against dependencies and commercialization in the digital attention economy. The Pope notes that AI developers are called to embed “transparency, responsibility toward affected communities, and careful attention to ensuring that what is being cultivated is a genuine good” into their projects.

EU Institutions Move to Streamline AI Act Obligations

On May 7, 2026, the European Council and European Parliament reached a provisional agreement to streamline certain aspects of the EU AI Act as part of the broader Omnibus VII initiative.

The agreement proposes several targeted adjustments, including extending the timeline for the application of high-risk AI system obligations by up to 16 months. It also broadens certain regulatory exemptions previously available to small and medium-sized enterprises (SMEs), extending them to small mid-cap companies (SMCs). In limited circumstances, certain compliance obligations are reduced.

Additionally, the agreement expands allowances for processing sensitive personal data where necessary for bias detection and mitigation, reflecting a practical recognition of fairness challenges in AI systems. The role and powers of the EU AI Office are also reinforced.

The agreement remains subject to formal adoption by both institutions, which have indicated an intention to finalize the changes before August 2, 2026, when key provisions of the existing AI Act are set to take effect.

Hintze Law PLLC is a Chambers-ranked and Legal 500-recognized, boutique law firm that provides counseling exclusively on data protection including AI, privacy, and data security. Hintze attorneys and data consultants support technology, advertising, media, fintech, health, biotech, ecommerce, and mobile industries.
Don’t Sleep on Maryland: The Maryland Online Data Privacy Act Will Keep Health and Wellness Companies Up at Night — Hintze